The whole security lifecycle in one place

Requirements, risk analysis, testing, monitoring and the evidence for your auditor, connected from the first design to decommissioning.

Two levels, one platform

Security officers see the whole organisation. Engineering teams work project by project. Both read the same data.

Across the organisation

Oversight of security maturity for the CISO and the security officers.

ConfigurationIT, OT and product ISMS adapted to you, with company templates, milestones, the organigram and escalation paths.
GRC and KPI dashboardSupplier assessments and supply-chain risk, tracked across the company.
Assessments and auditsGlobal audits and compliance tracking, project assessments and design reviews.
Central managementProgrammes, requirements and the software and hardware libraries, managed in one place.

In every project

A guided workflow through each phase of development and compliance.

  1. 01
    RFI and RFQ planningProject configuration, cost analysis and development interface agreements.
  2. 02
    Risk analysisA preliminary risk assessment, then the full threat analysis and risk assessment.
  3. 03
    Build and validateSecurity architecture, security testing and validation.
  4. 04
    Deliver and maintainThe security assurance case, vulnerability and incident management, and maintenance.

From project creation to decommissioning, across a lifecycle of 20 years or more.

Analyse

Find the risk before it ships

Model the product as it is built, then let the analysis follow from the model.
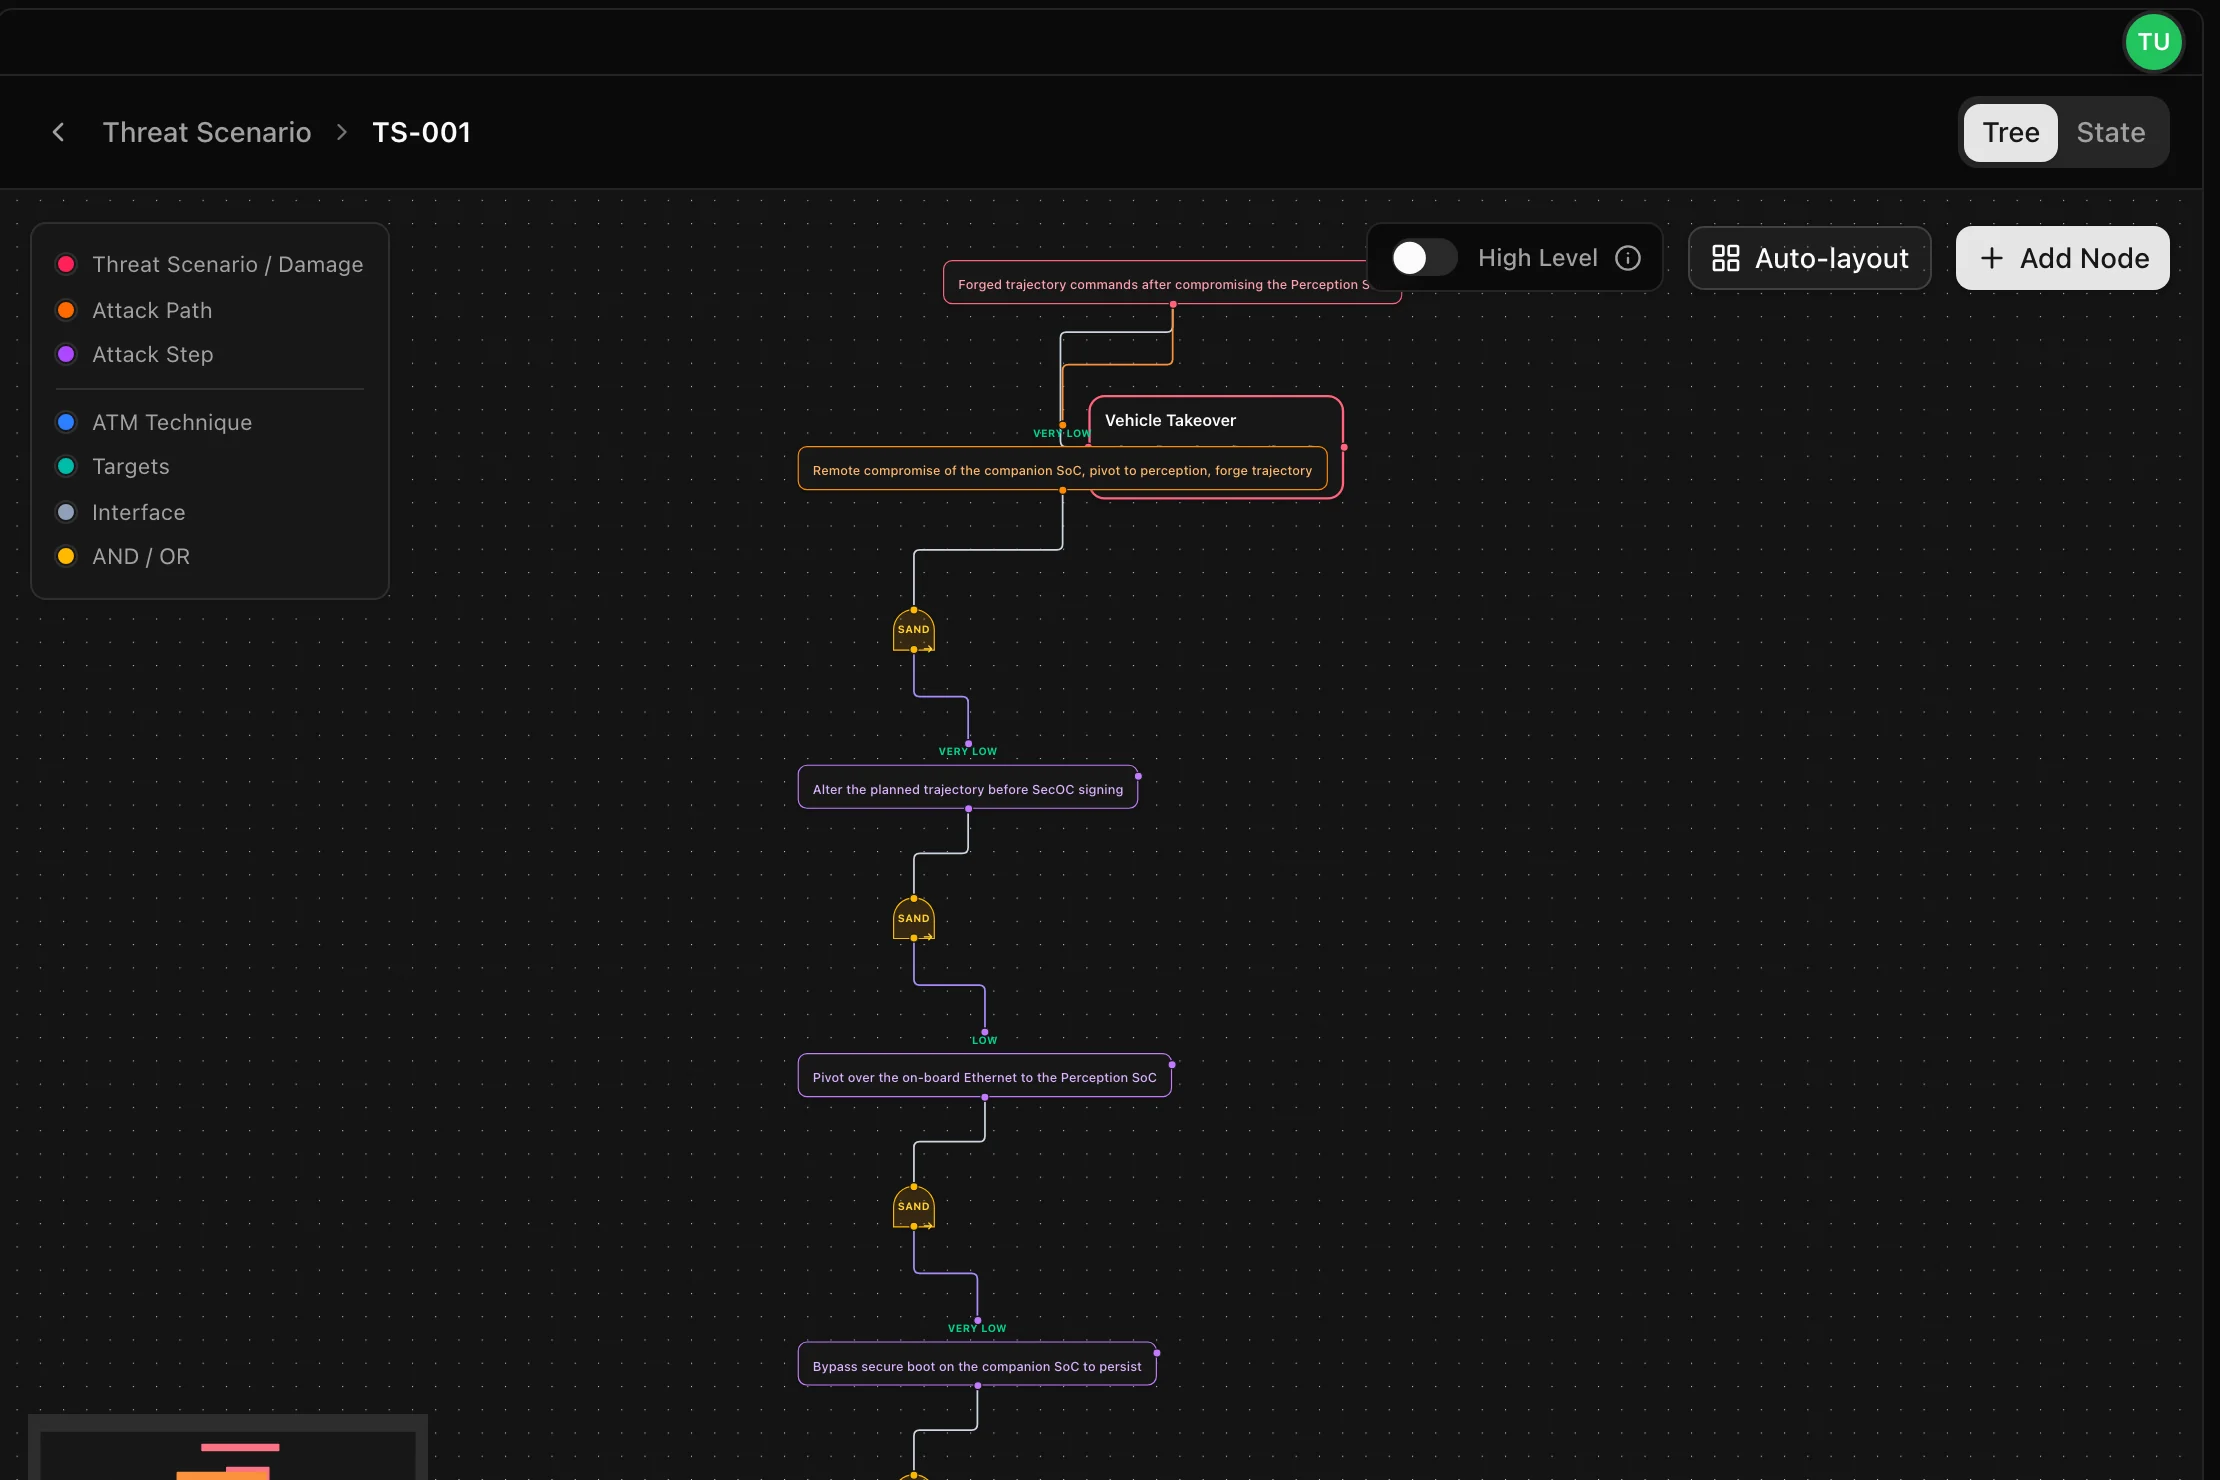
Threat analysisModel the system, its assets and the outside world, then derive damage scenarios, threat scenarios and risk under ISO/SAE 21434.
Attack pathsEach path is rated on the attack-potential factors of its steps, so feasibility is derived, never typed.
IEC 62443 goalsHold each zone and conduit to its target security level and see the gap per foundational requirement.
Security conceptsTurn treated risks into goals, concepts and the requirements that implement them.
An attack tree in SecBerg Core, each step rated on its attack-potential factors.

Monitor

Know what an advisory means for you

New vulnerabilities land every day. Only the ones that reach your products should reach your teams.
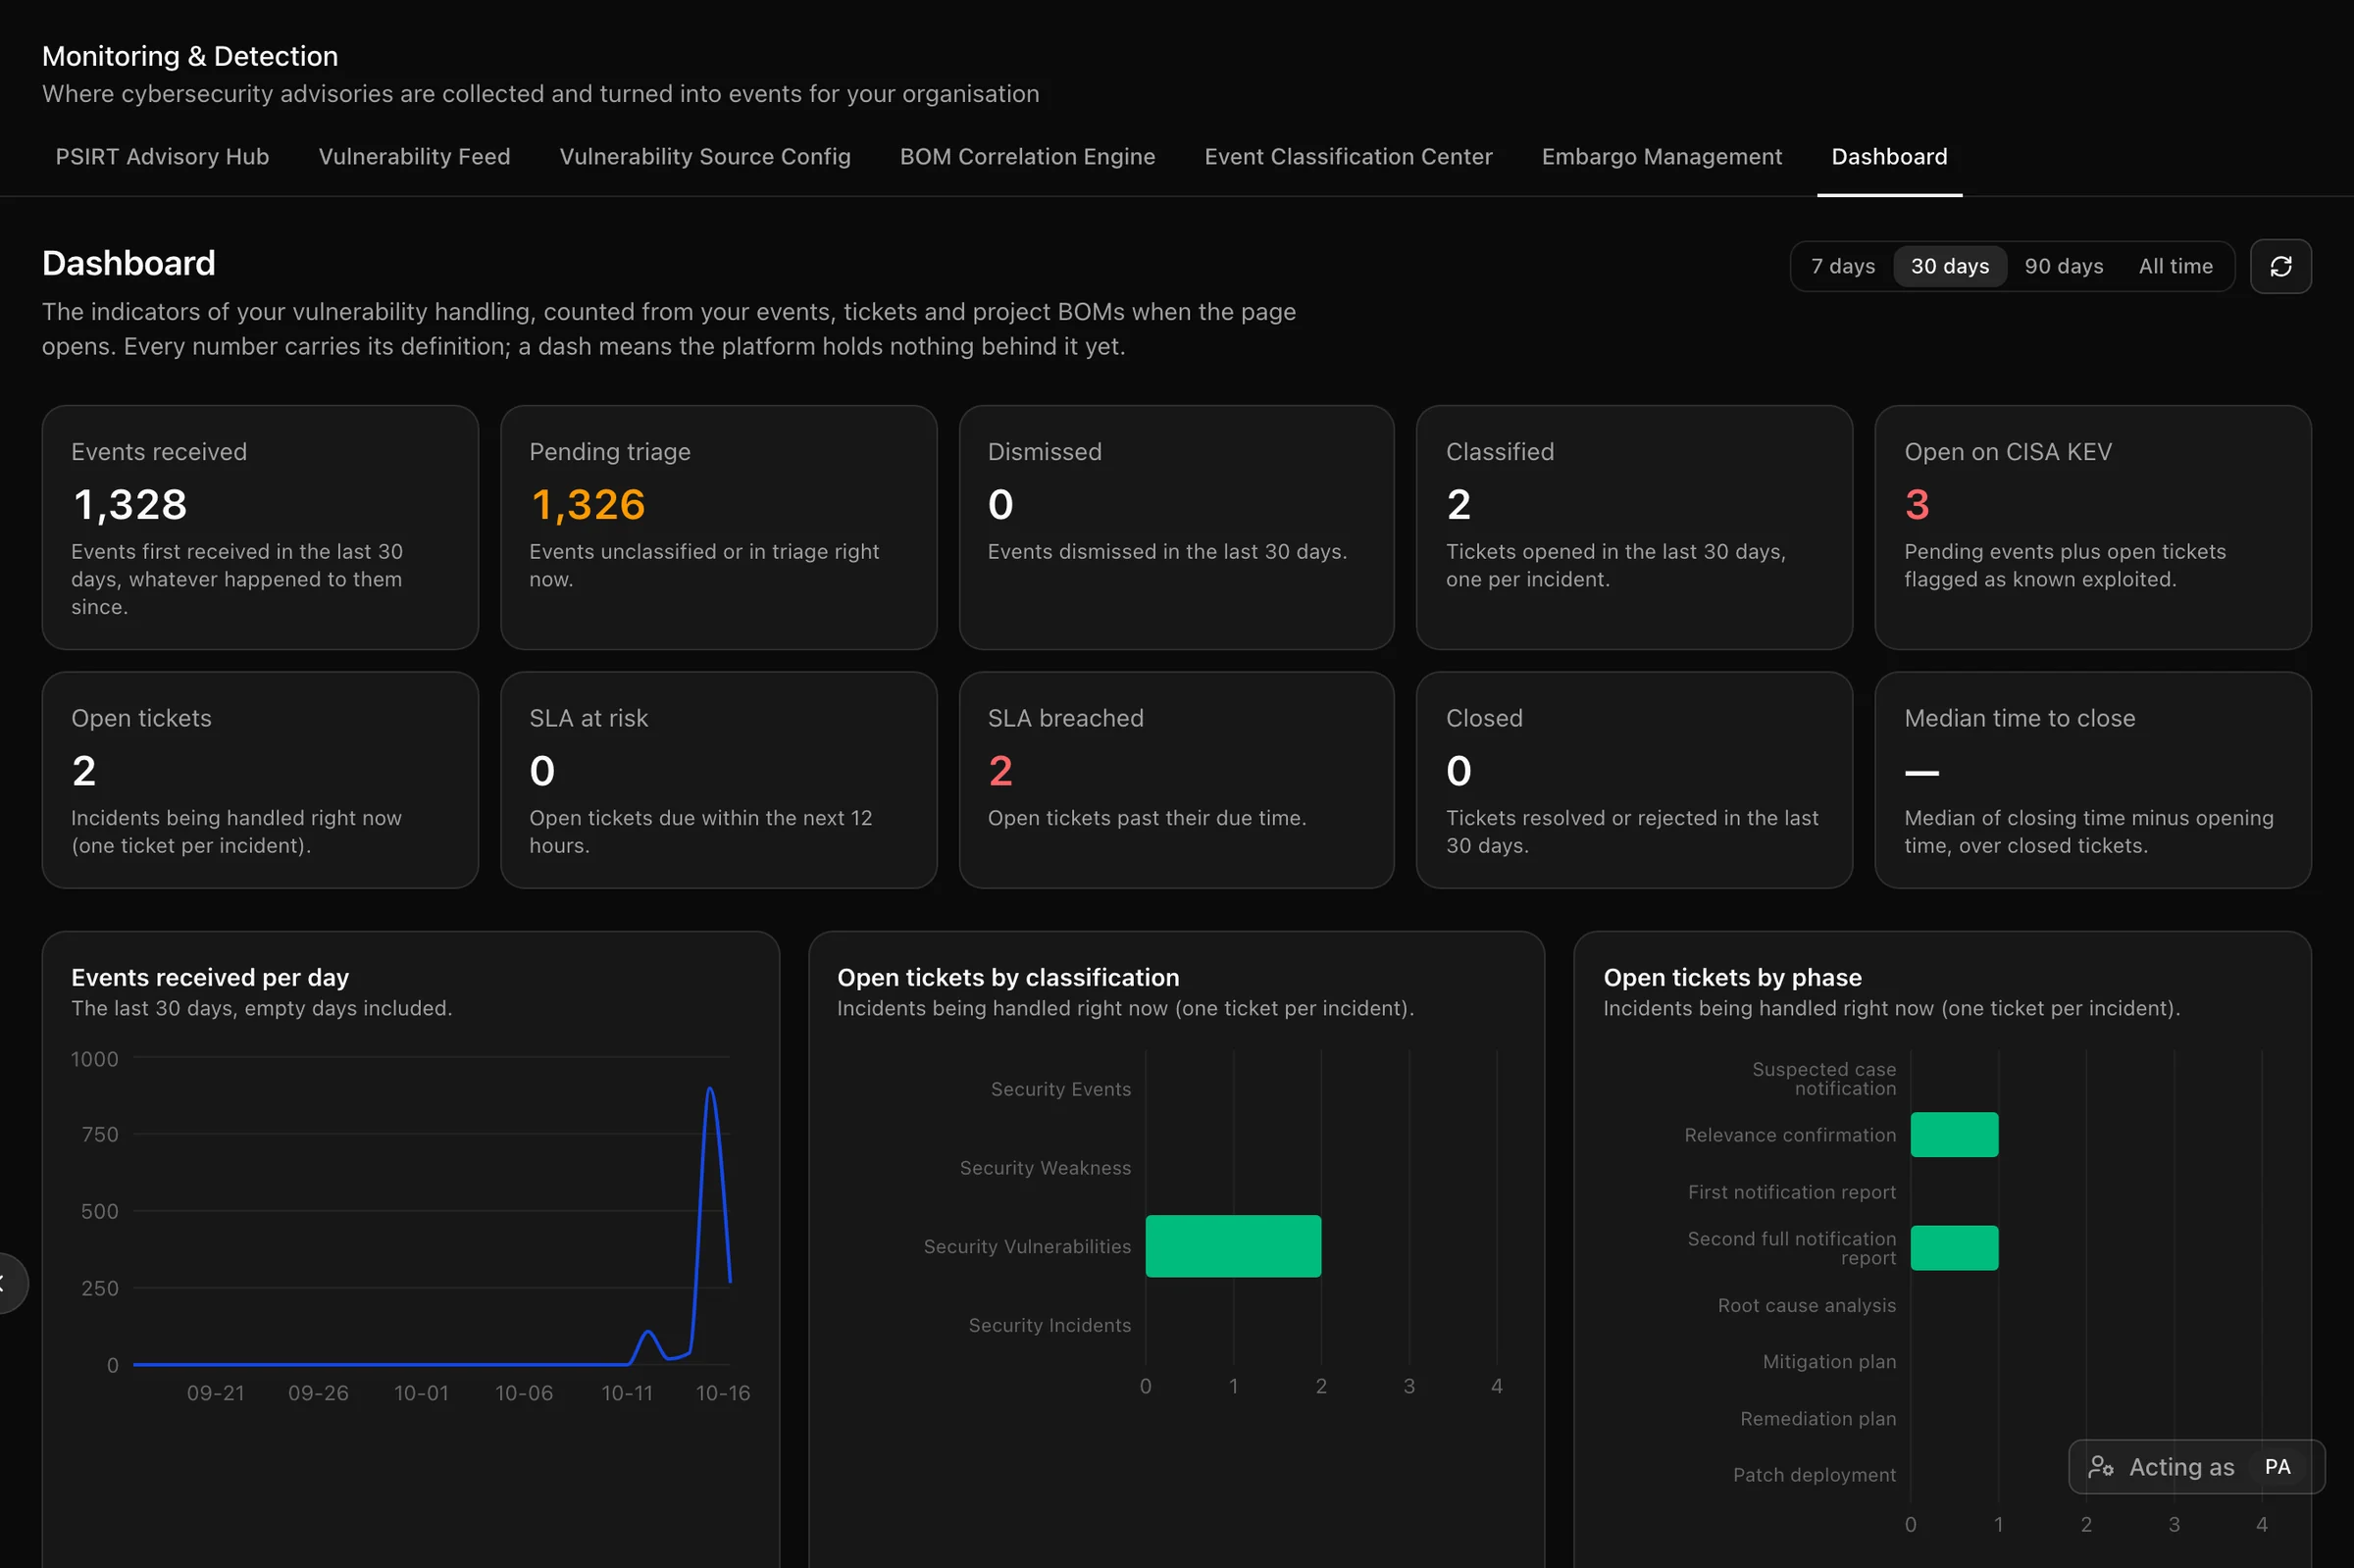
SDO CenterAdvisories from national CERTs, chip-vendor PSIRTs and open-source projects, matched to what each programme ships.
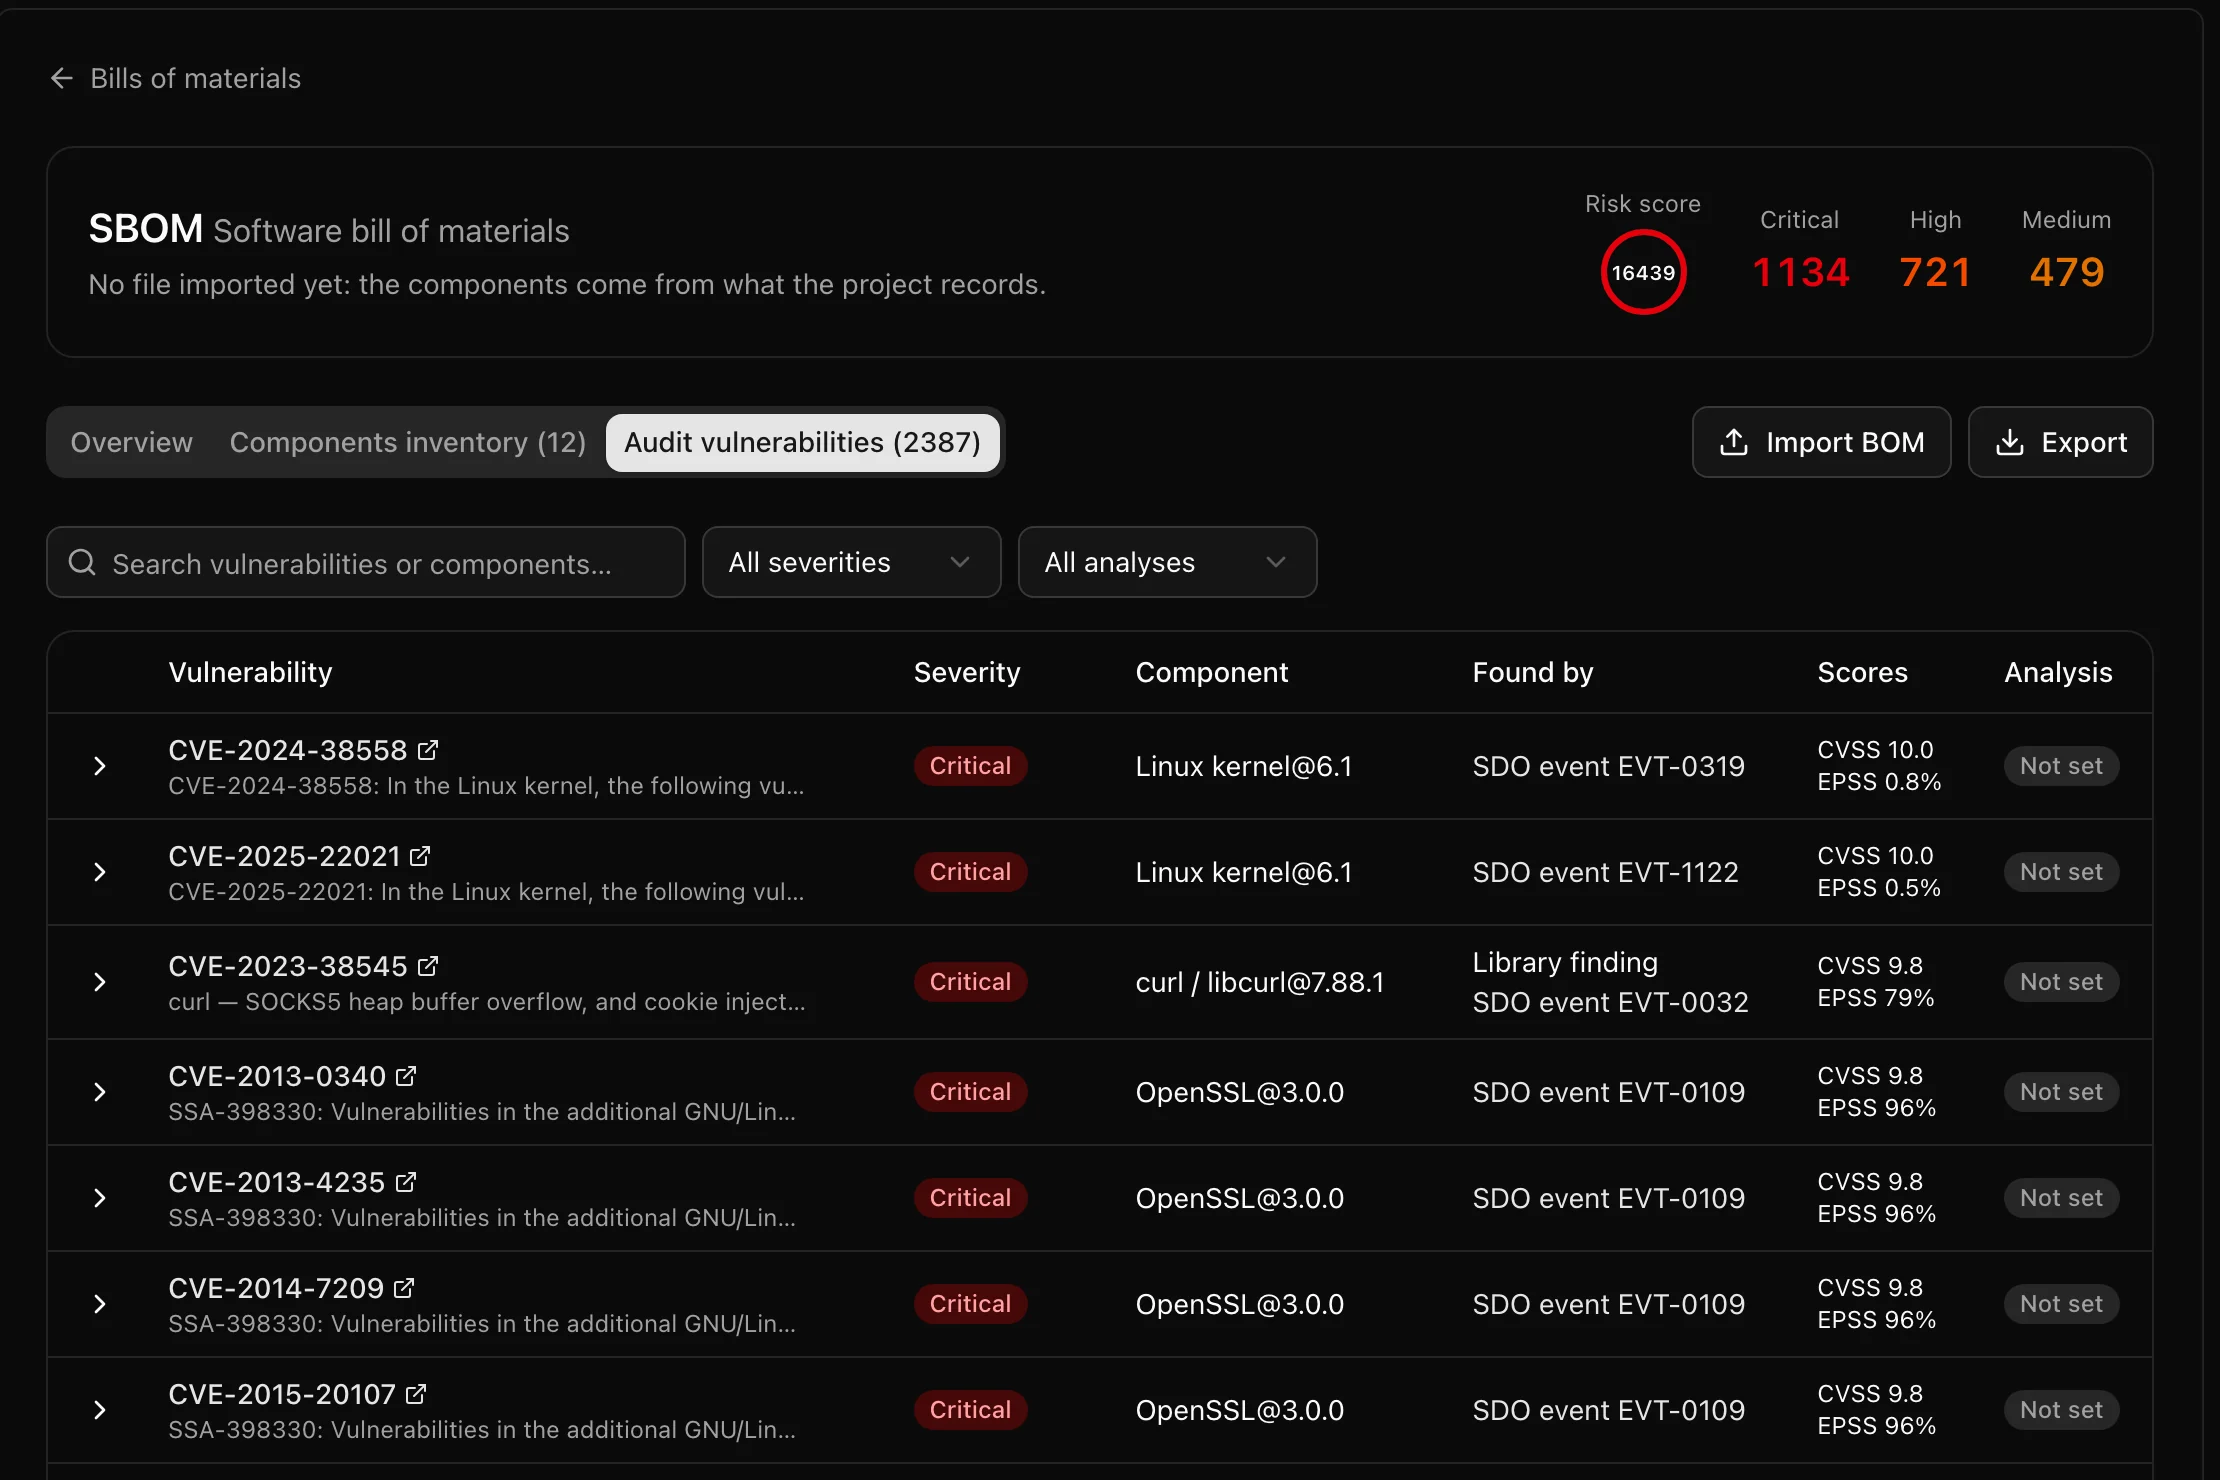
Bills of materialsHardware, software and cryptographic BOMs built from the model and kept current against new advisories.
Owner alertsOnly the owners of an affected part hear about it. Everyone else keeps working.
The SDO Center listing advisories matched to the programmes that ship the affected parts.

Prove

Hand your auditor the proof

The evidence is a by-product of the work, not a document written after it.
Security caseAn argument for why the product is secure, linked to the evidence behind every claim.
RequirementsRequirements traced end to end, from the stakeholder down to the test that verifies them.
Reviews and gatesPhase reviews with checklists, tickets and approval gates, with every change on the audit ledger.
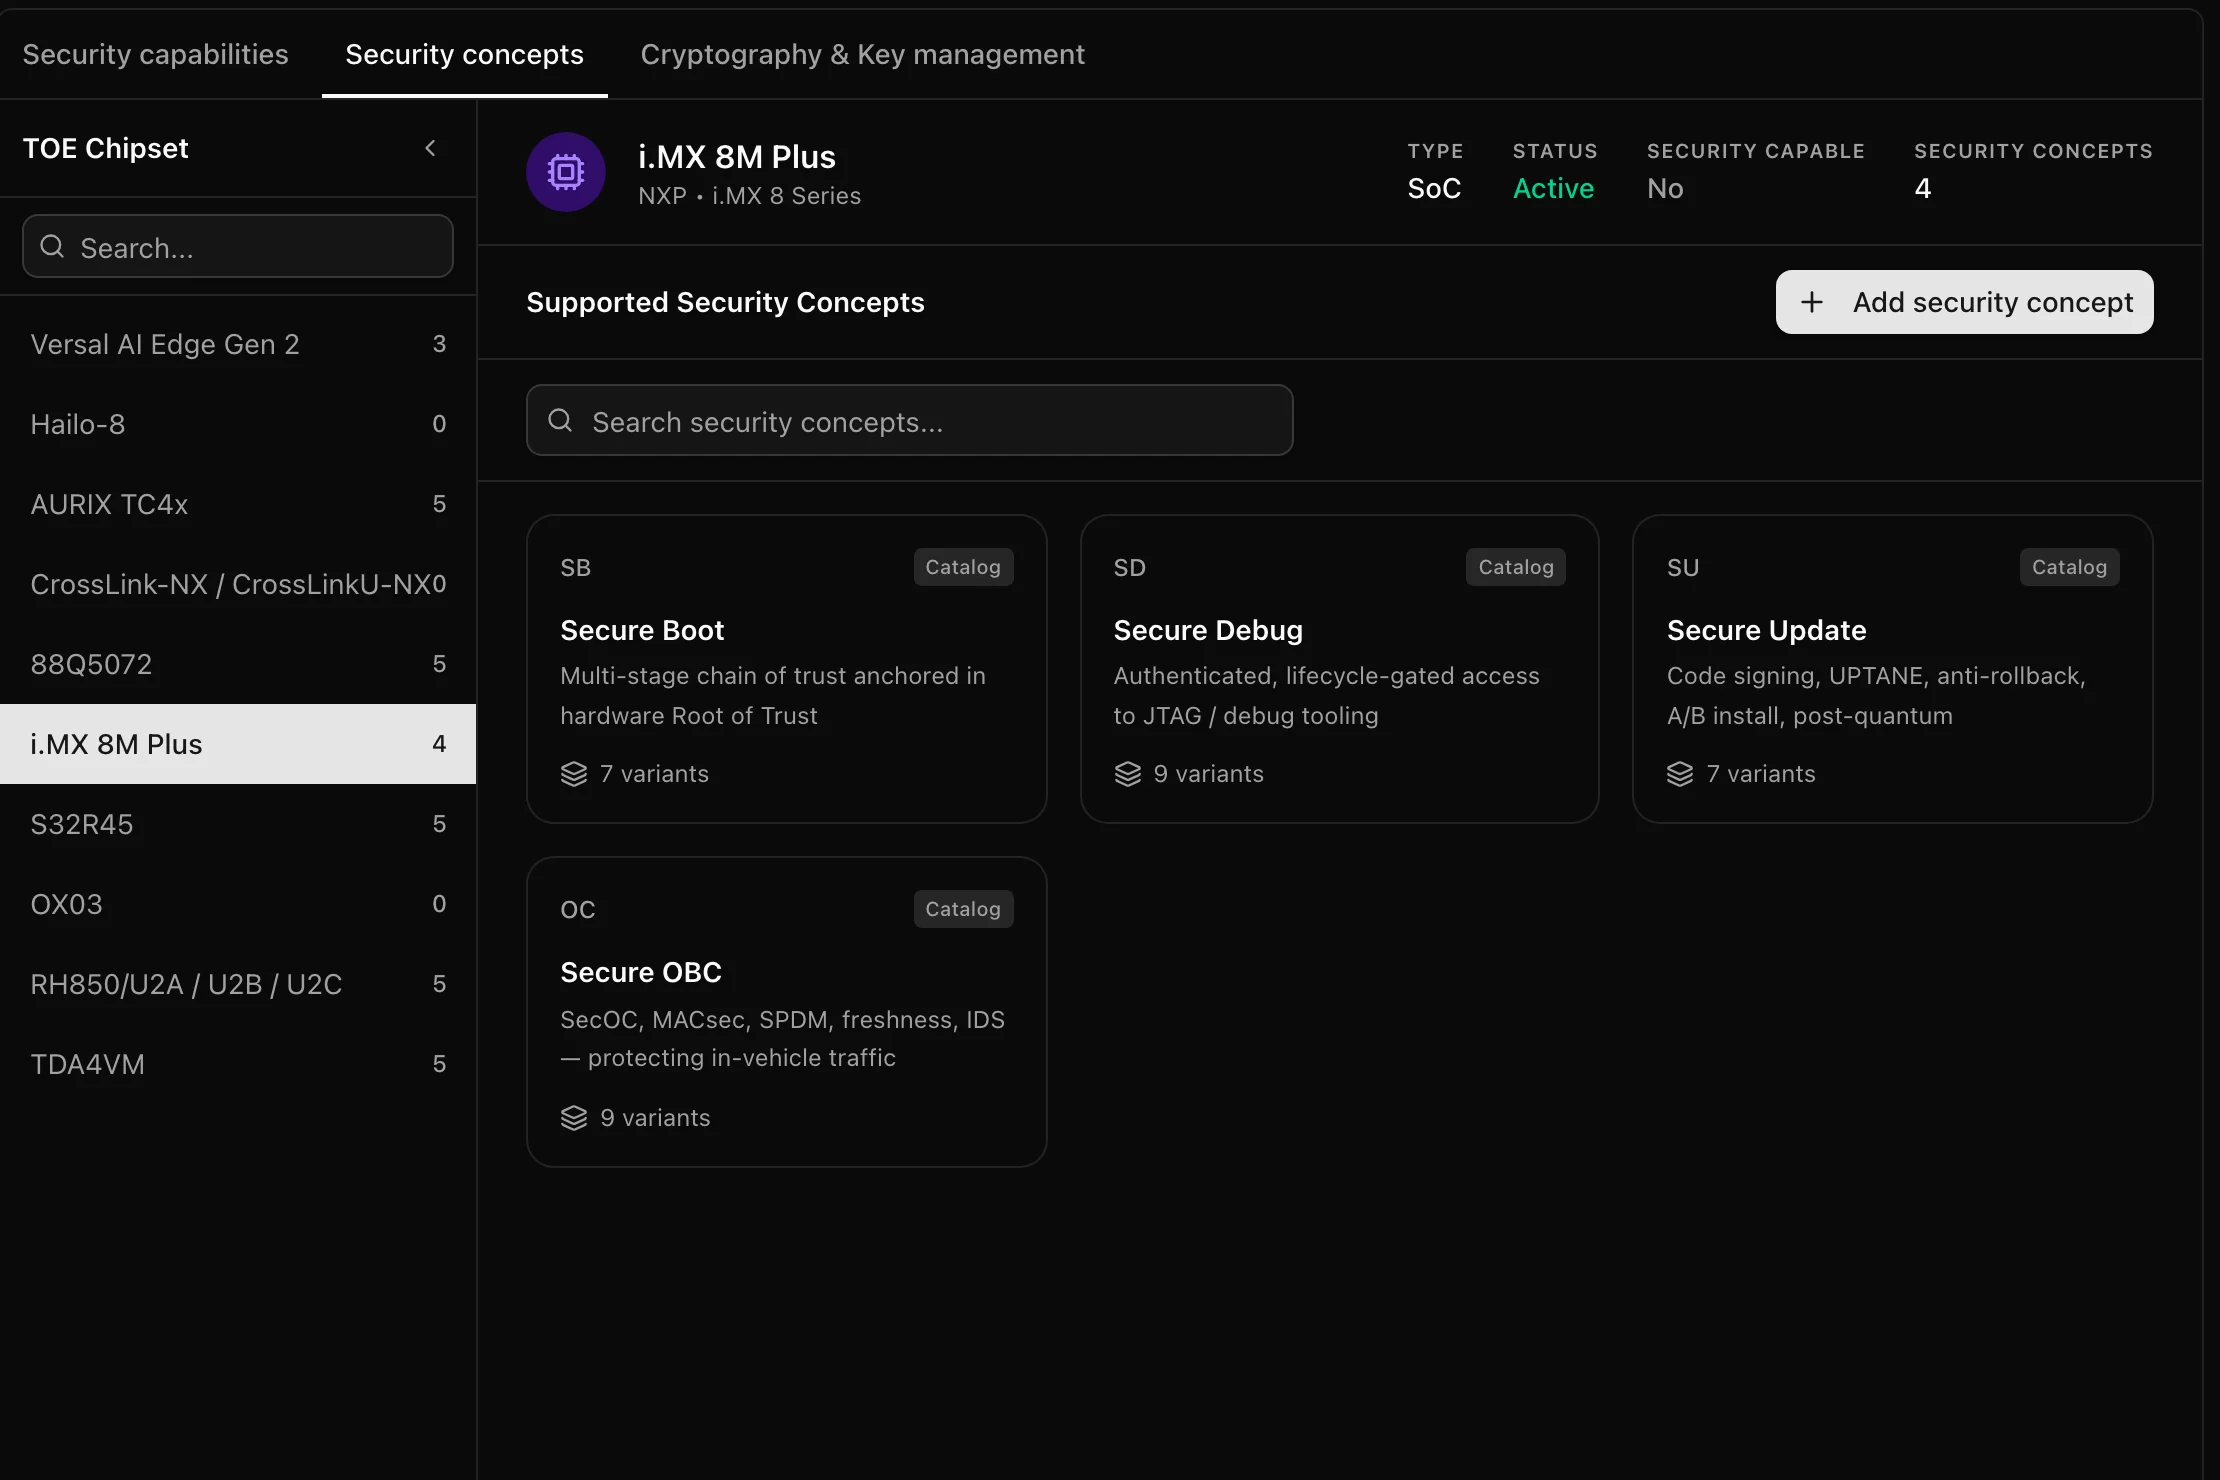
Security concepts linked to the goals and requirements they implement.

Test

Test what you built

Security testing runs against the requirements it verifies, with agents doing the slow parts.

Security testingFunctional testing, static analysis, fuzzing and secure code review, tracked against the requirements they verify.
Secure code reviewAgents review the code and track it against MISRA and CERT C and C++.
Patch and retestA weakness that is found gets a proposed patch, and the patch is tested again before it ships.

Connect

Bring in suppliers and your tools

Security work crosses company lines. The model goes with it.
SuppliersGive a supplier their part of the model, with its own reviews and interface agreements.
Component librariesChipsets and software components with their security capabilities, reused across programmes.
IntegrationsWork stays in sync with Jira, Polarion, DOORS Next, GitLab and ServiceNow.
A bill of materials built from the system model, with each part's versions.

Agent

The TARA agent works across all of it

Name the product and the standard. The agent plans the work, draws the system, finds the attack paths and rates the risk, then hands you a draft to approve.

20+Connected modules
16+Specialised AI agents
4Industries: automotive, rail, maritime and industrial
20+Years of lifecycle, from creation to decommissioning

Start with
one programme

Live within a month. Proven on real work within three.

  1. 01
    Book a workshopBring one programme and the standards it answers to.
  2. 02
    Model it togetherOur engineers build it with yours, live in the platform.
  3. 03
    Run the pilotReal work, real evidence, signed off in three months.