
Blog
Regulation, engineering and the advisories worth knowing about.
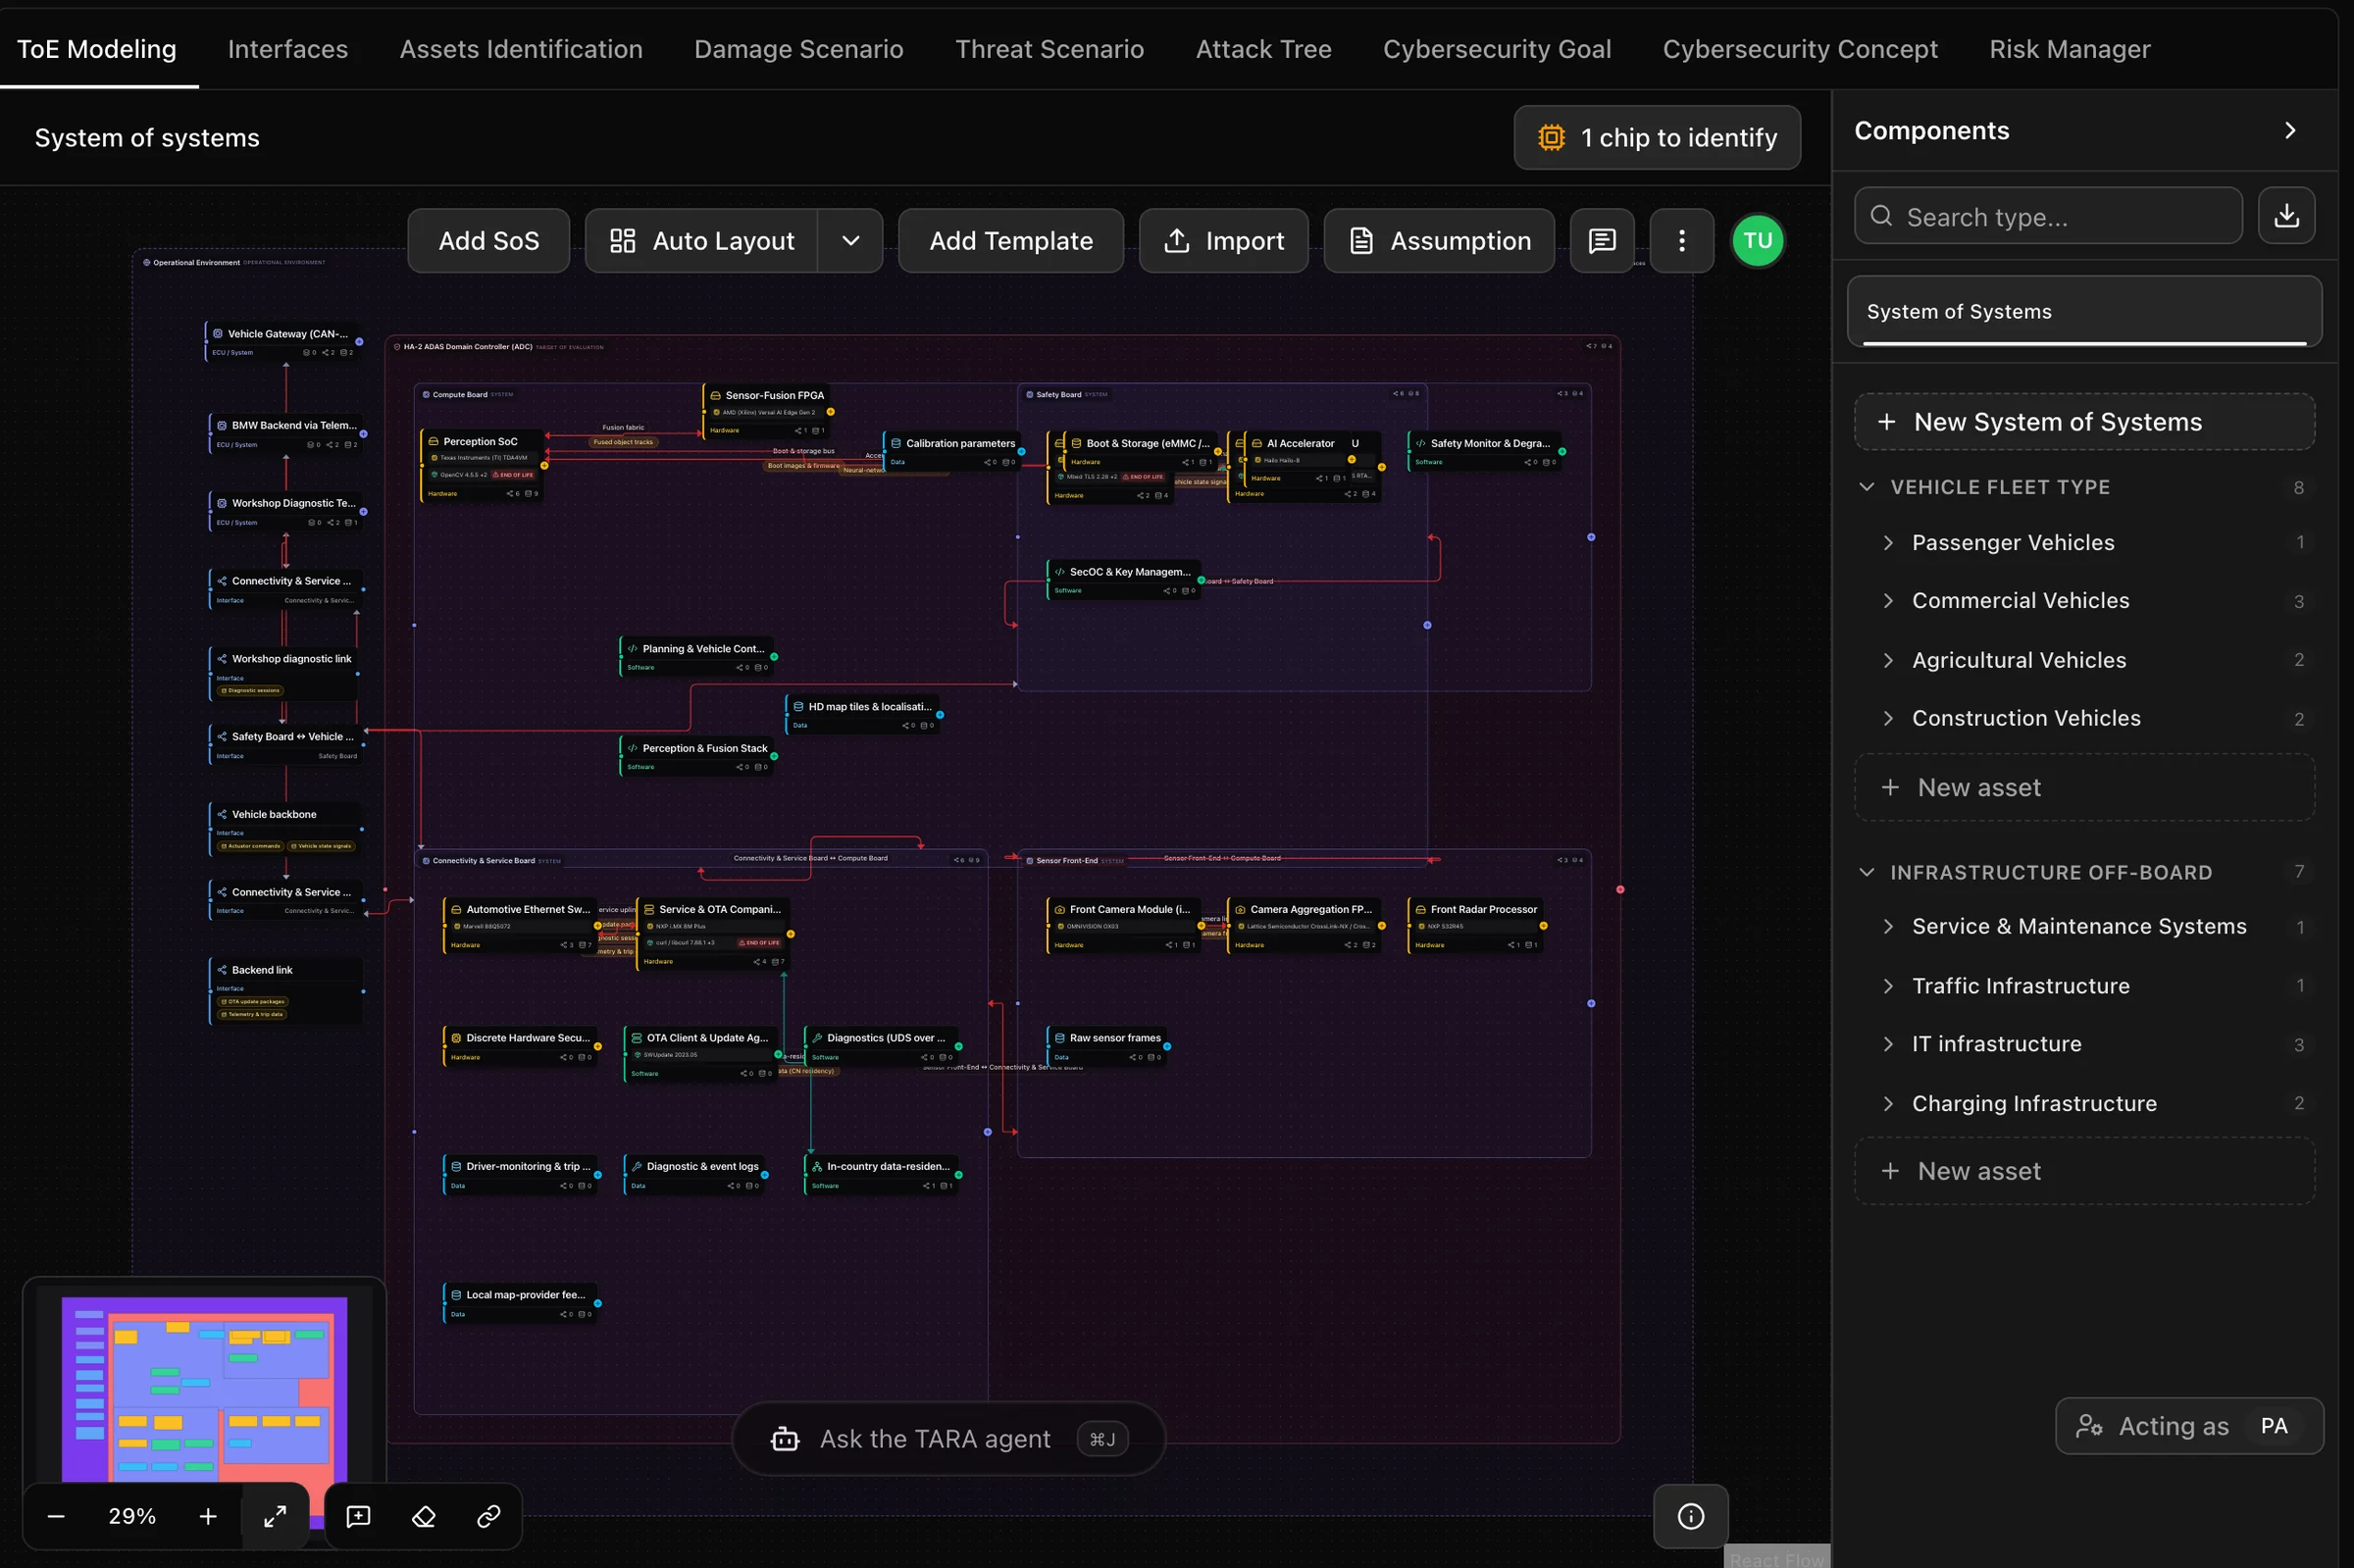
The TARA agent now shows its plan
Before it touches the model, the agent writes its plan and ticks it off step by step, so you always know what it is doing.
 Regulation
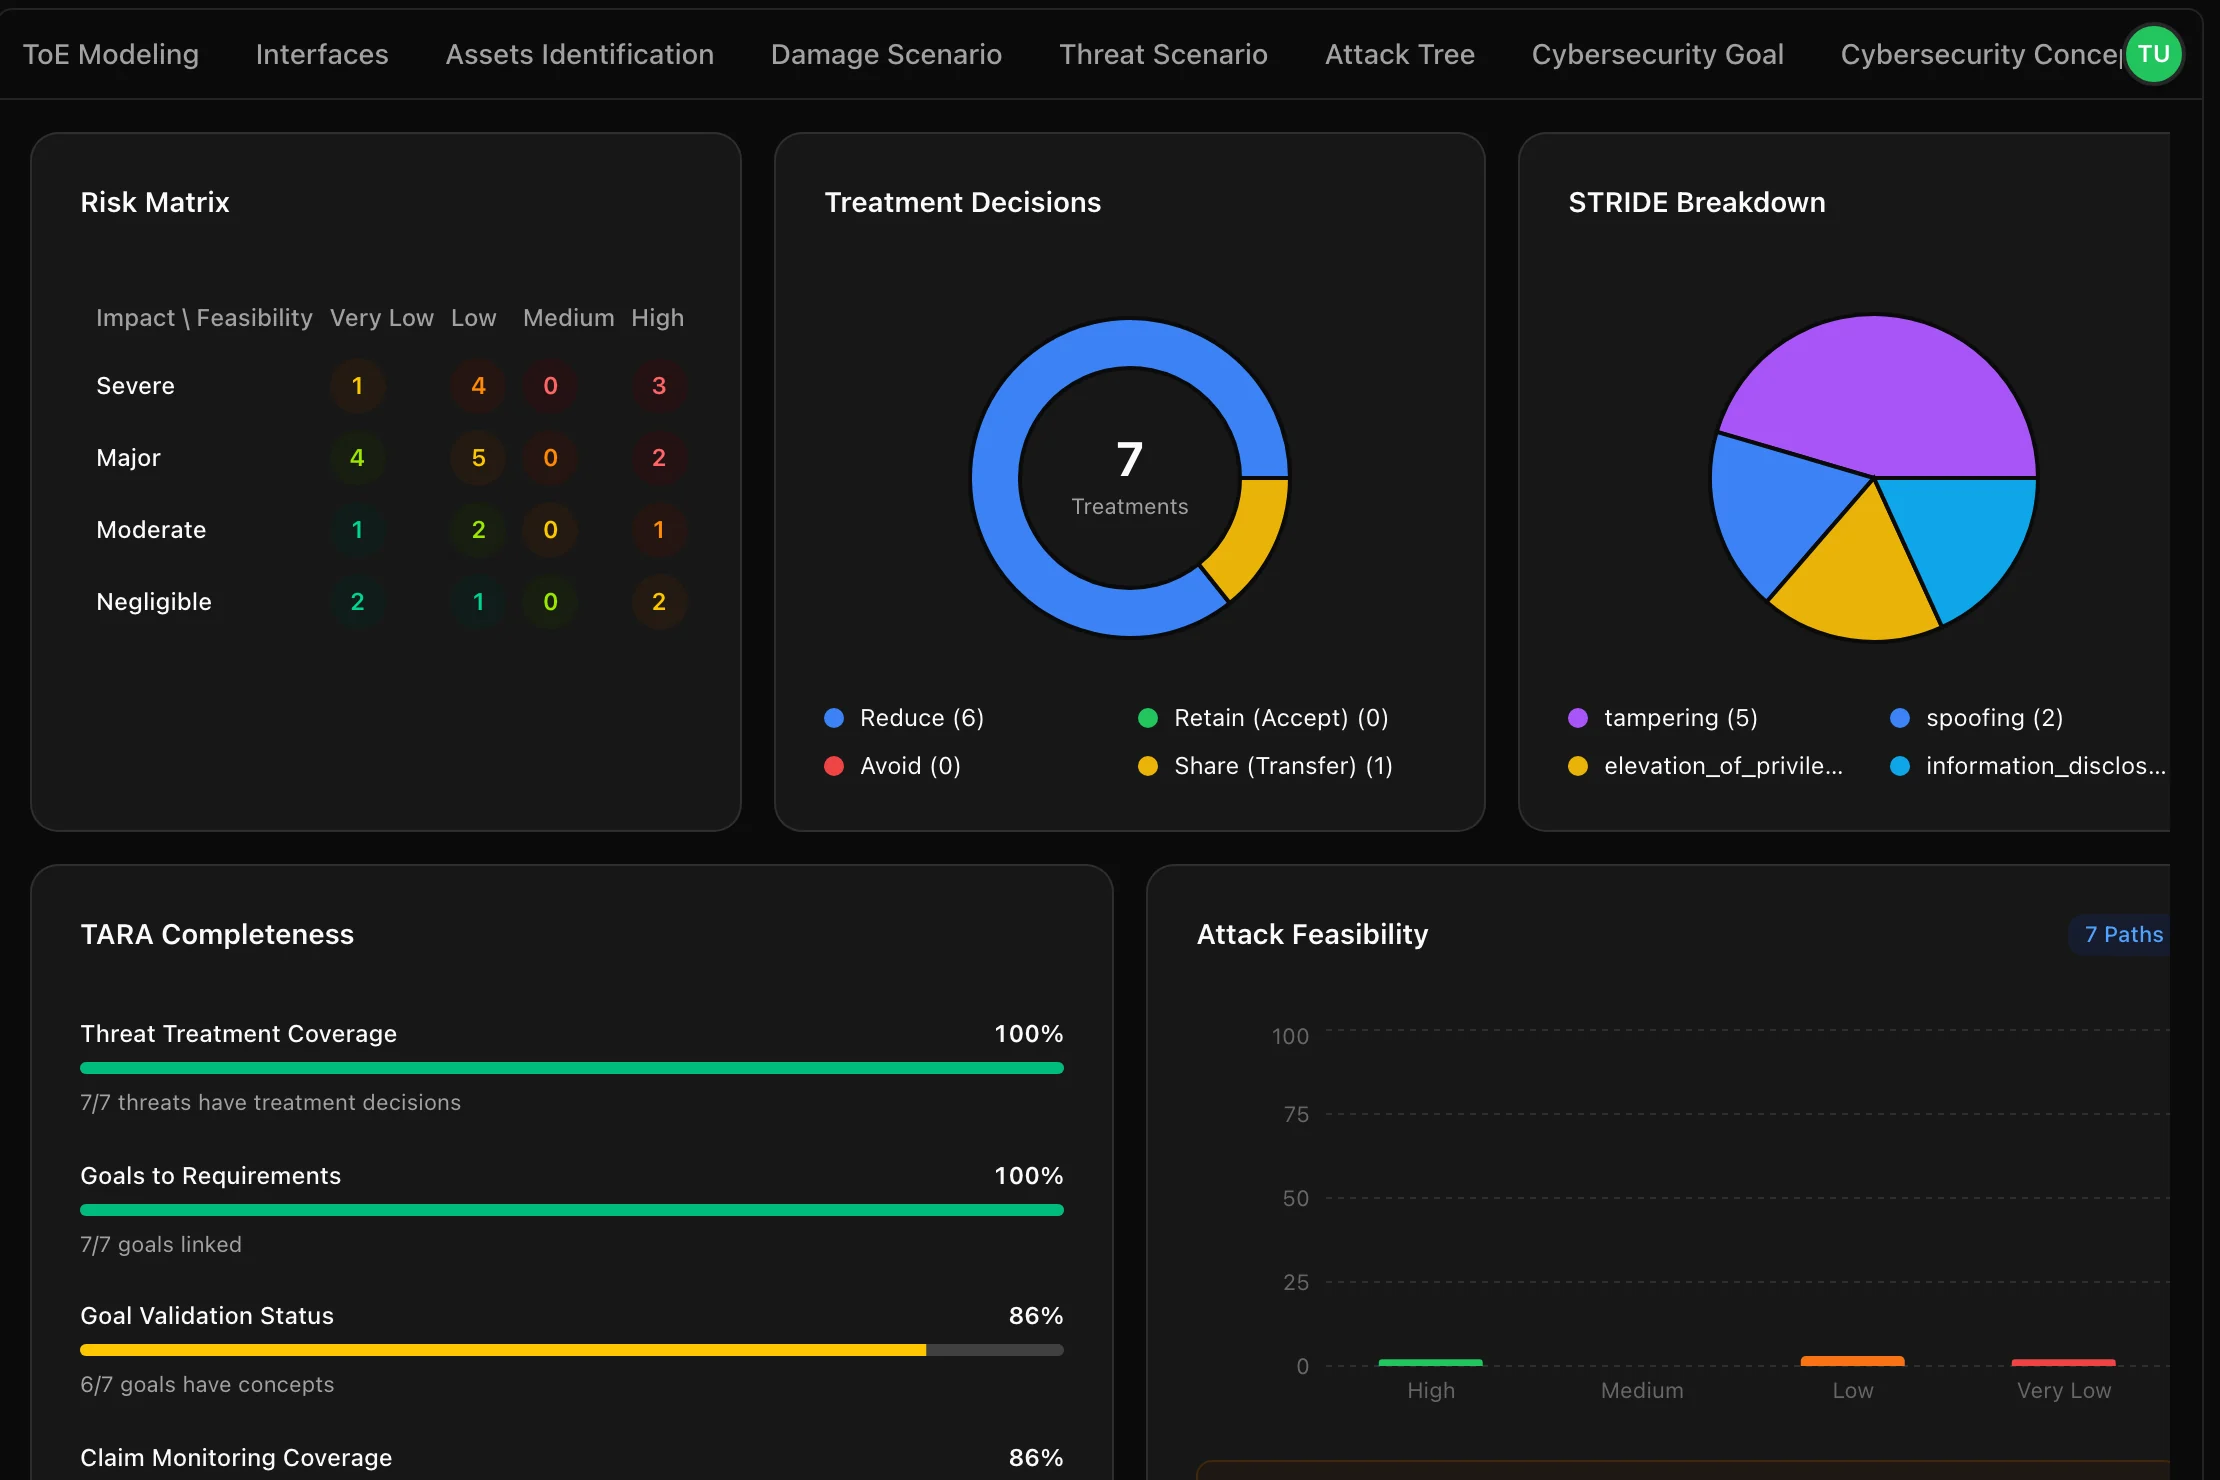
What a UNECE R155 auditor asks to see
The evidence an approval authority looks for, and where each piece lives in a connected model.
 Engineering
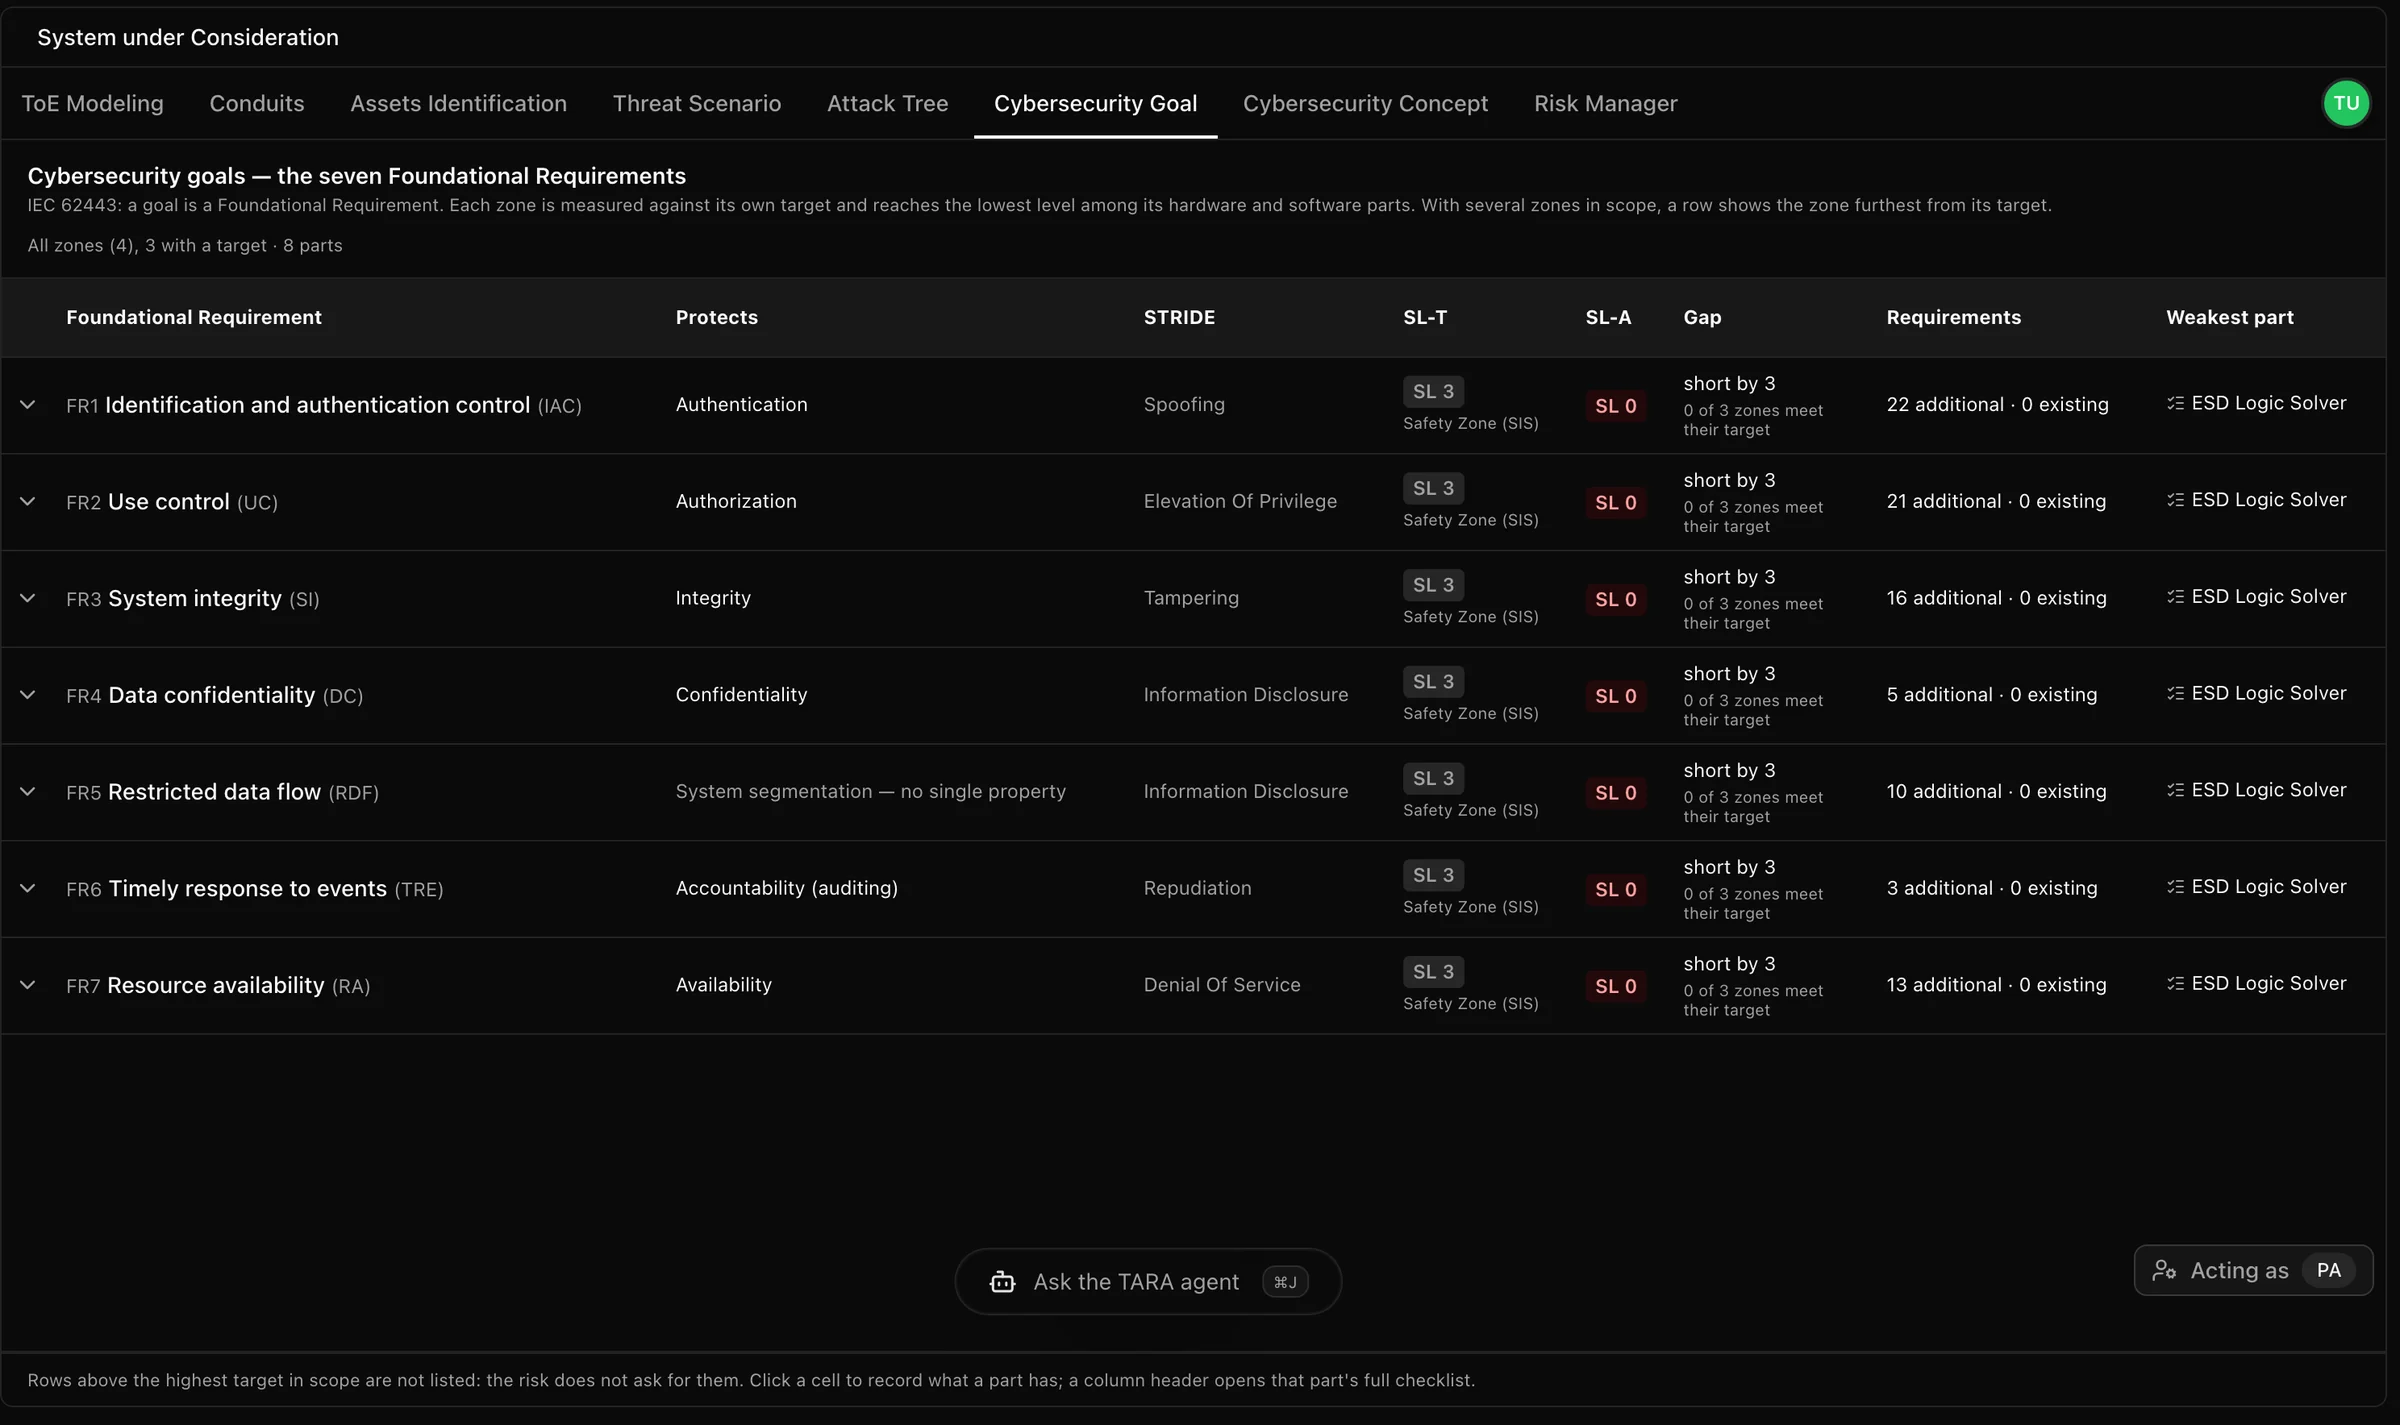
Setting SL-T per zone under IEC 62443-3-2
How to pick a target security level for each zone, and read the gap per foundational requirement.
 Vulnerabilities
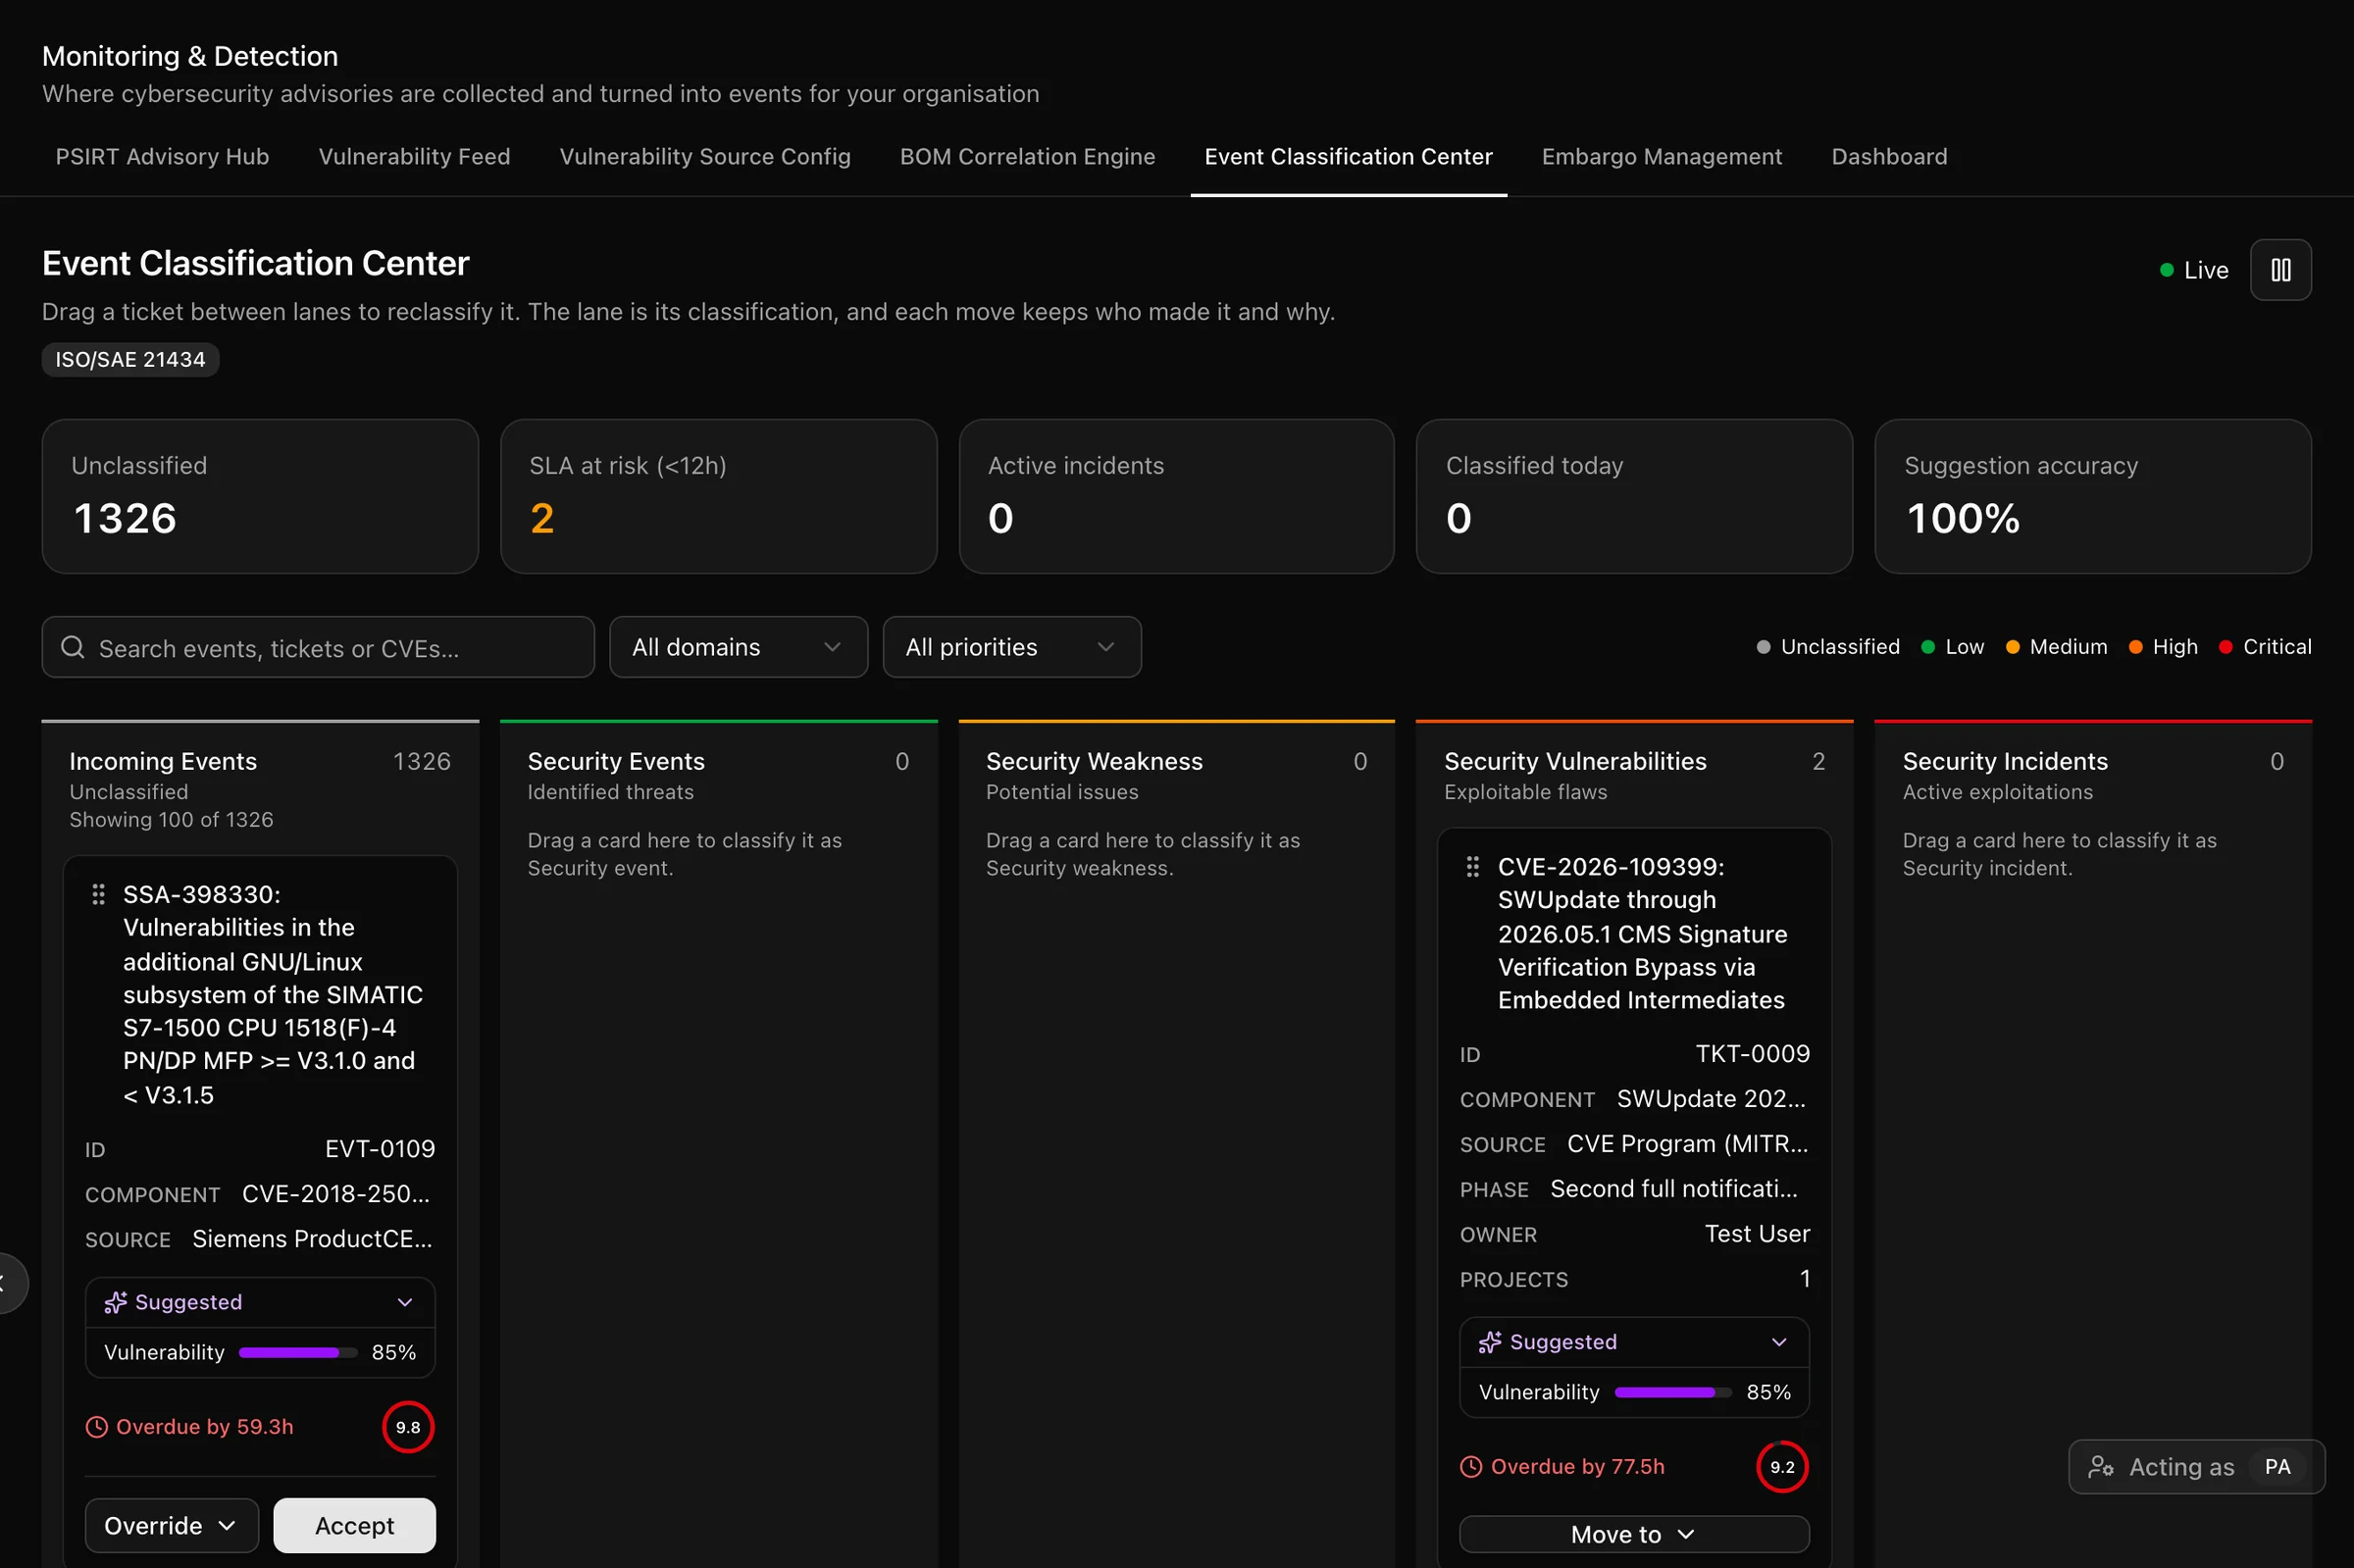
One advisory, two programmes: matching CVEs to your BOM
Why an advisory is only useful once you know which products ship the affected component.
 Engineering
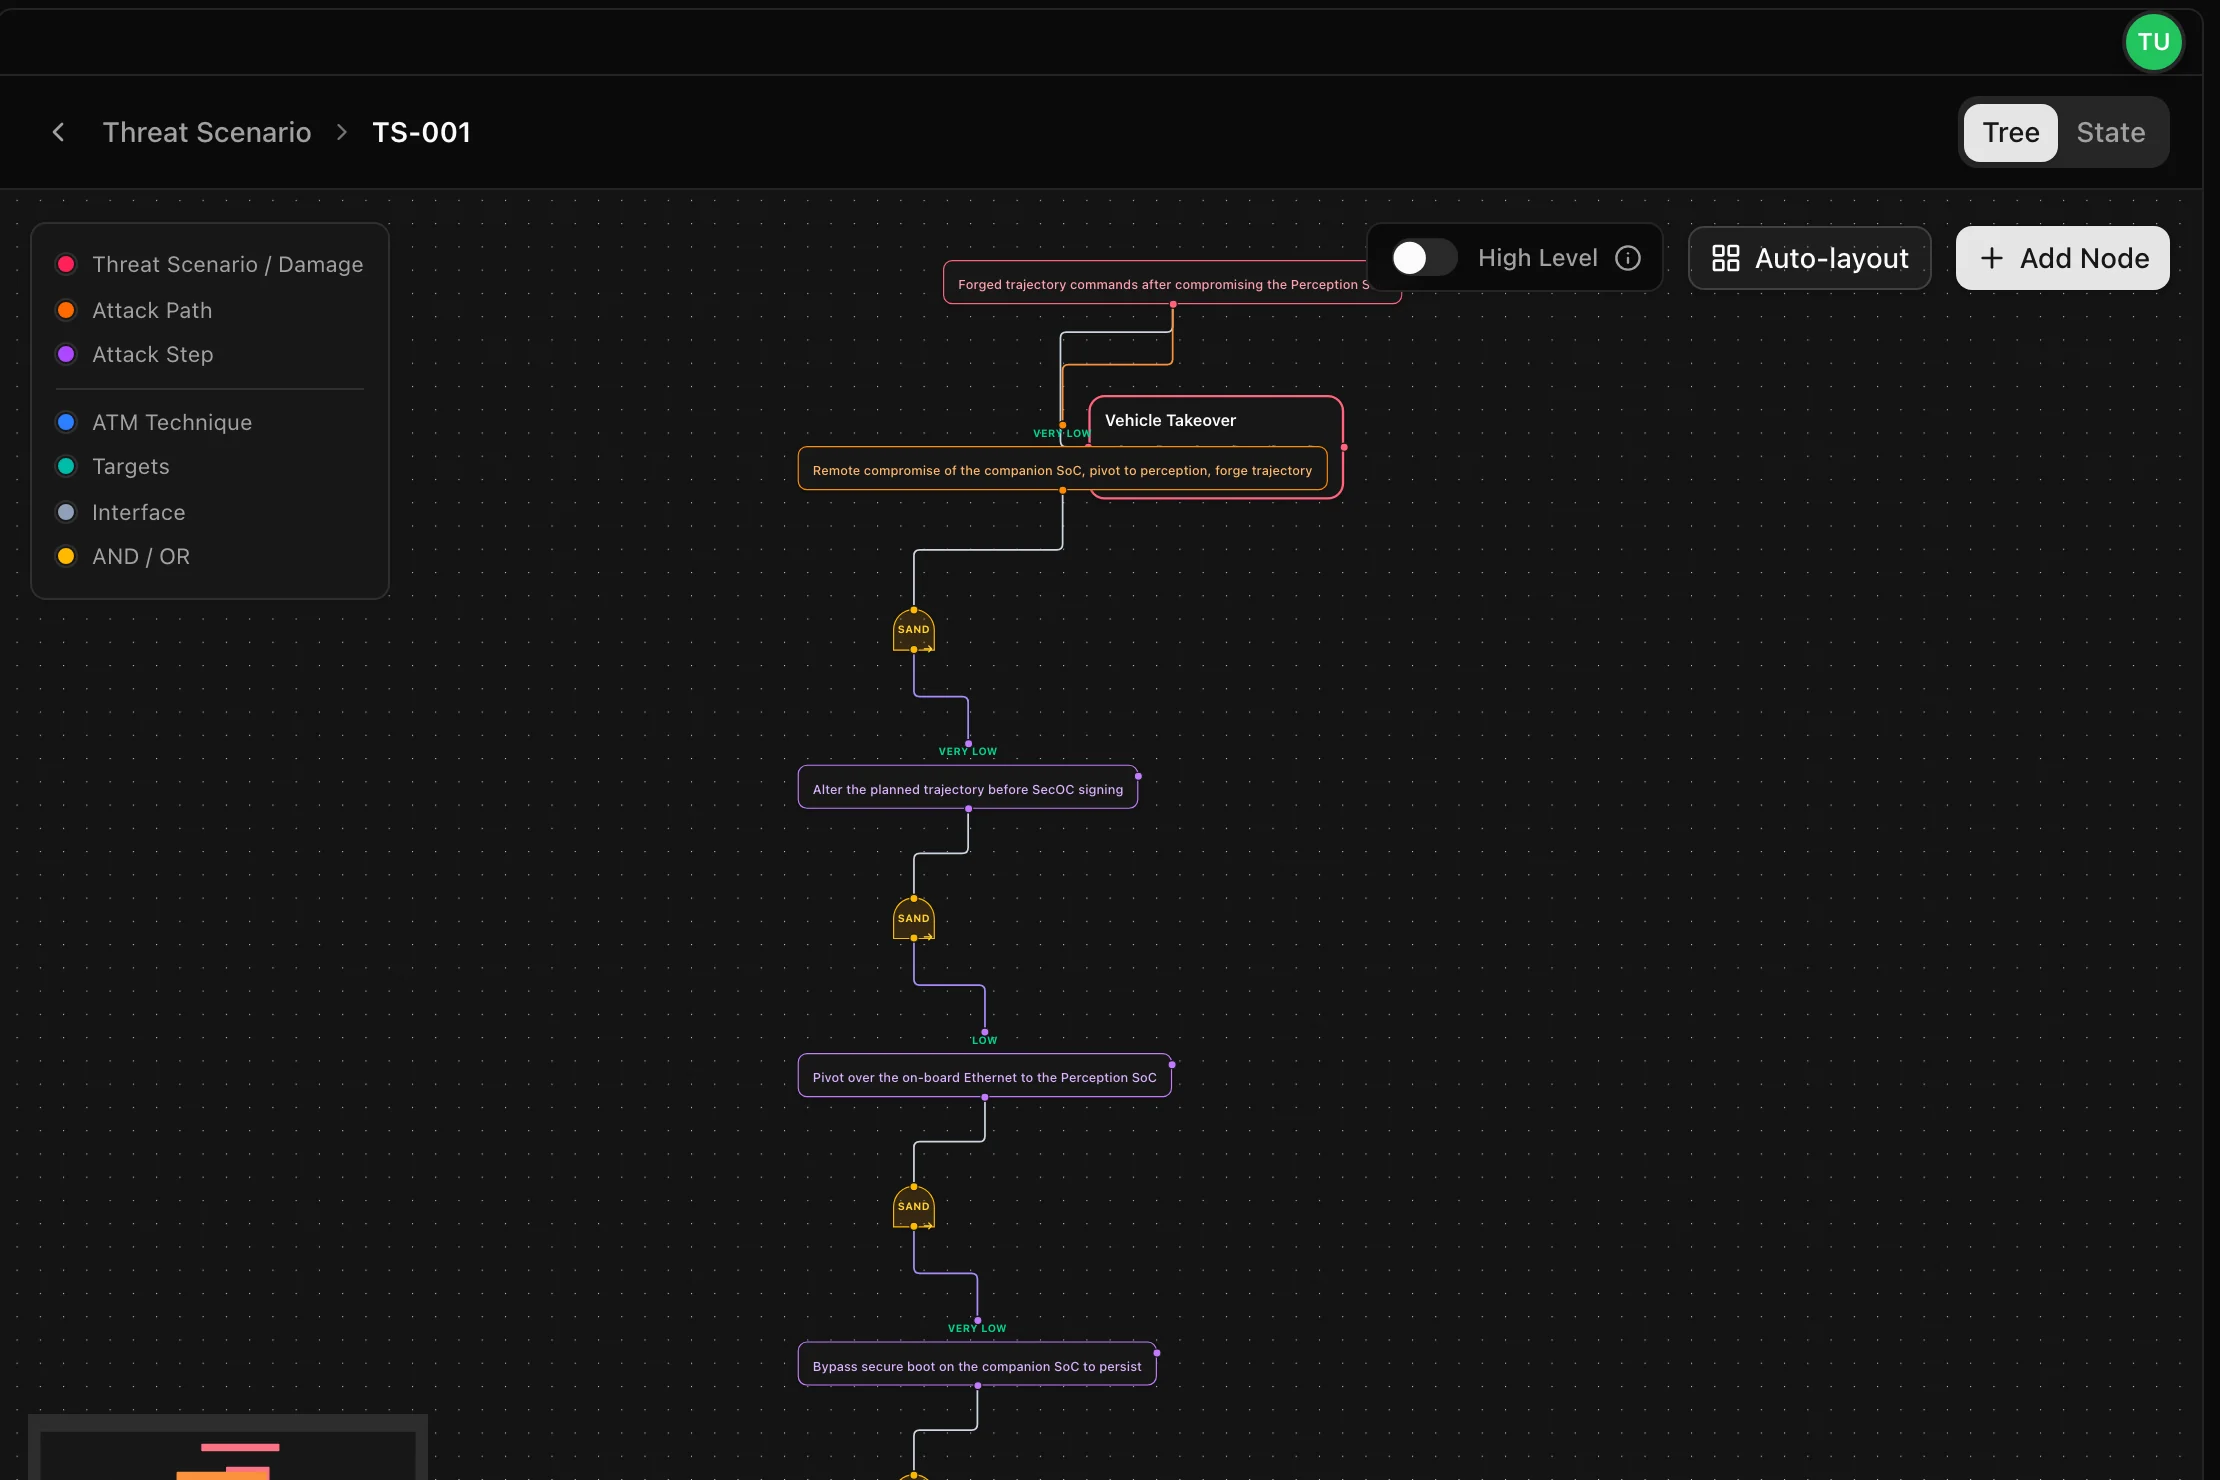
Feasibility should be derived, never typed
Rating attack paths on the five attack-potential factors, and why the number must come from the steps.
 Regulation
CLC/TS 50701 and IEC 63452 for rail suppliers
What the rail standards ask of a supplier, and how they build on IEC 62443.
 Vulnerabilities
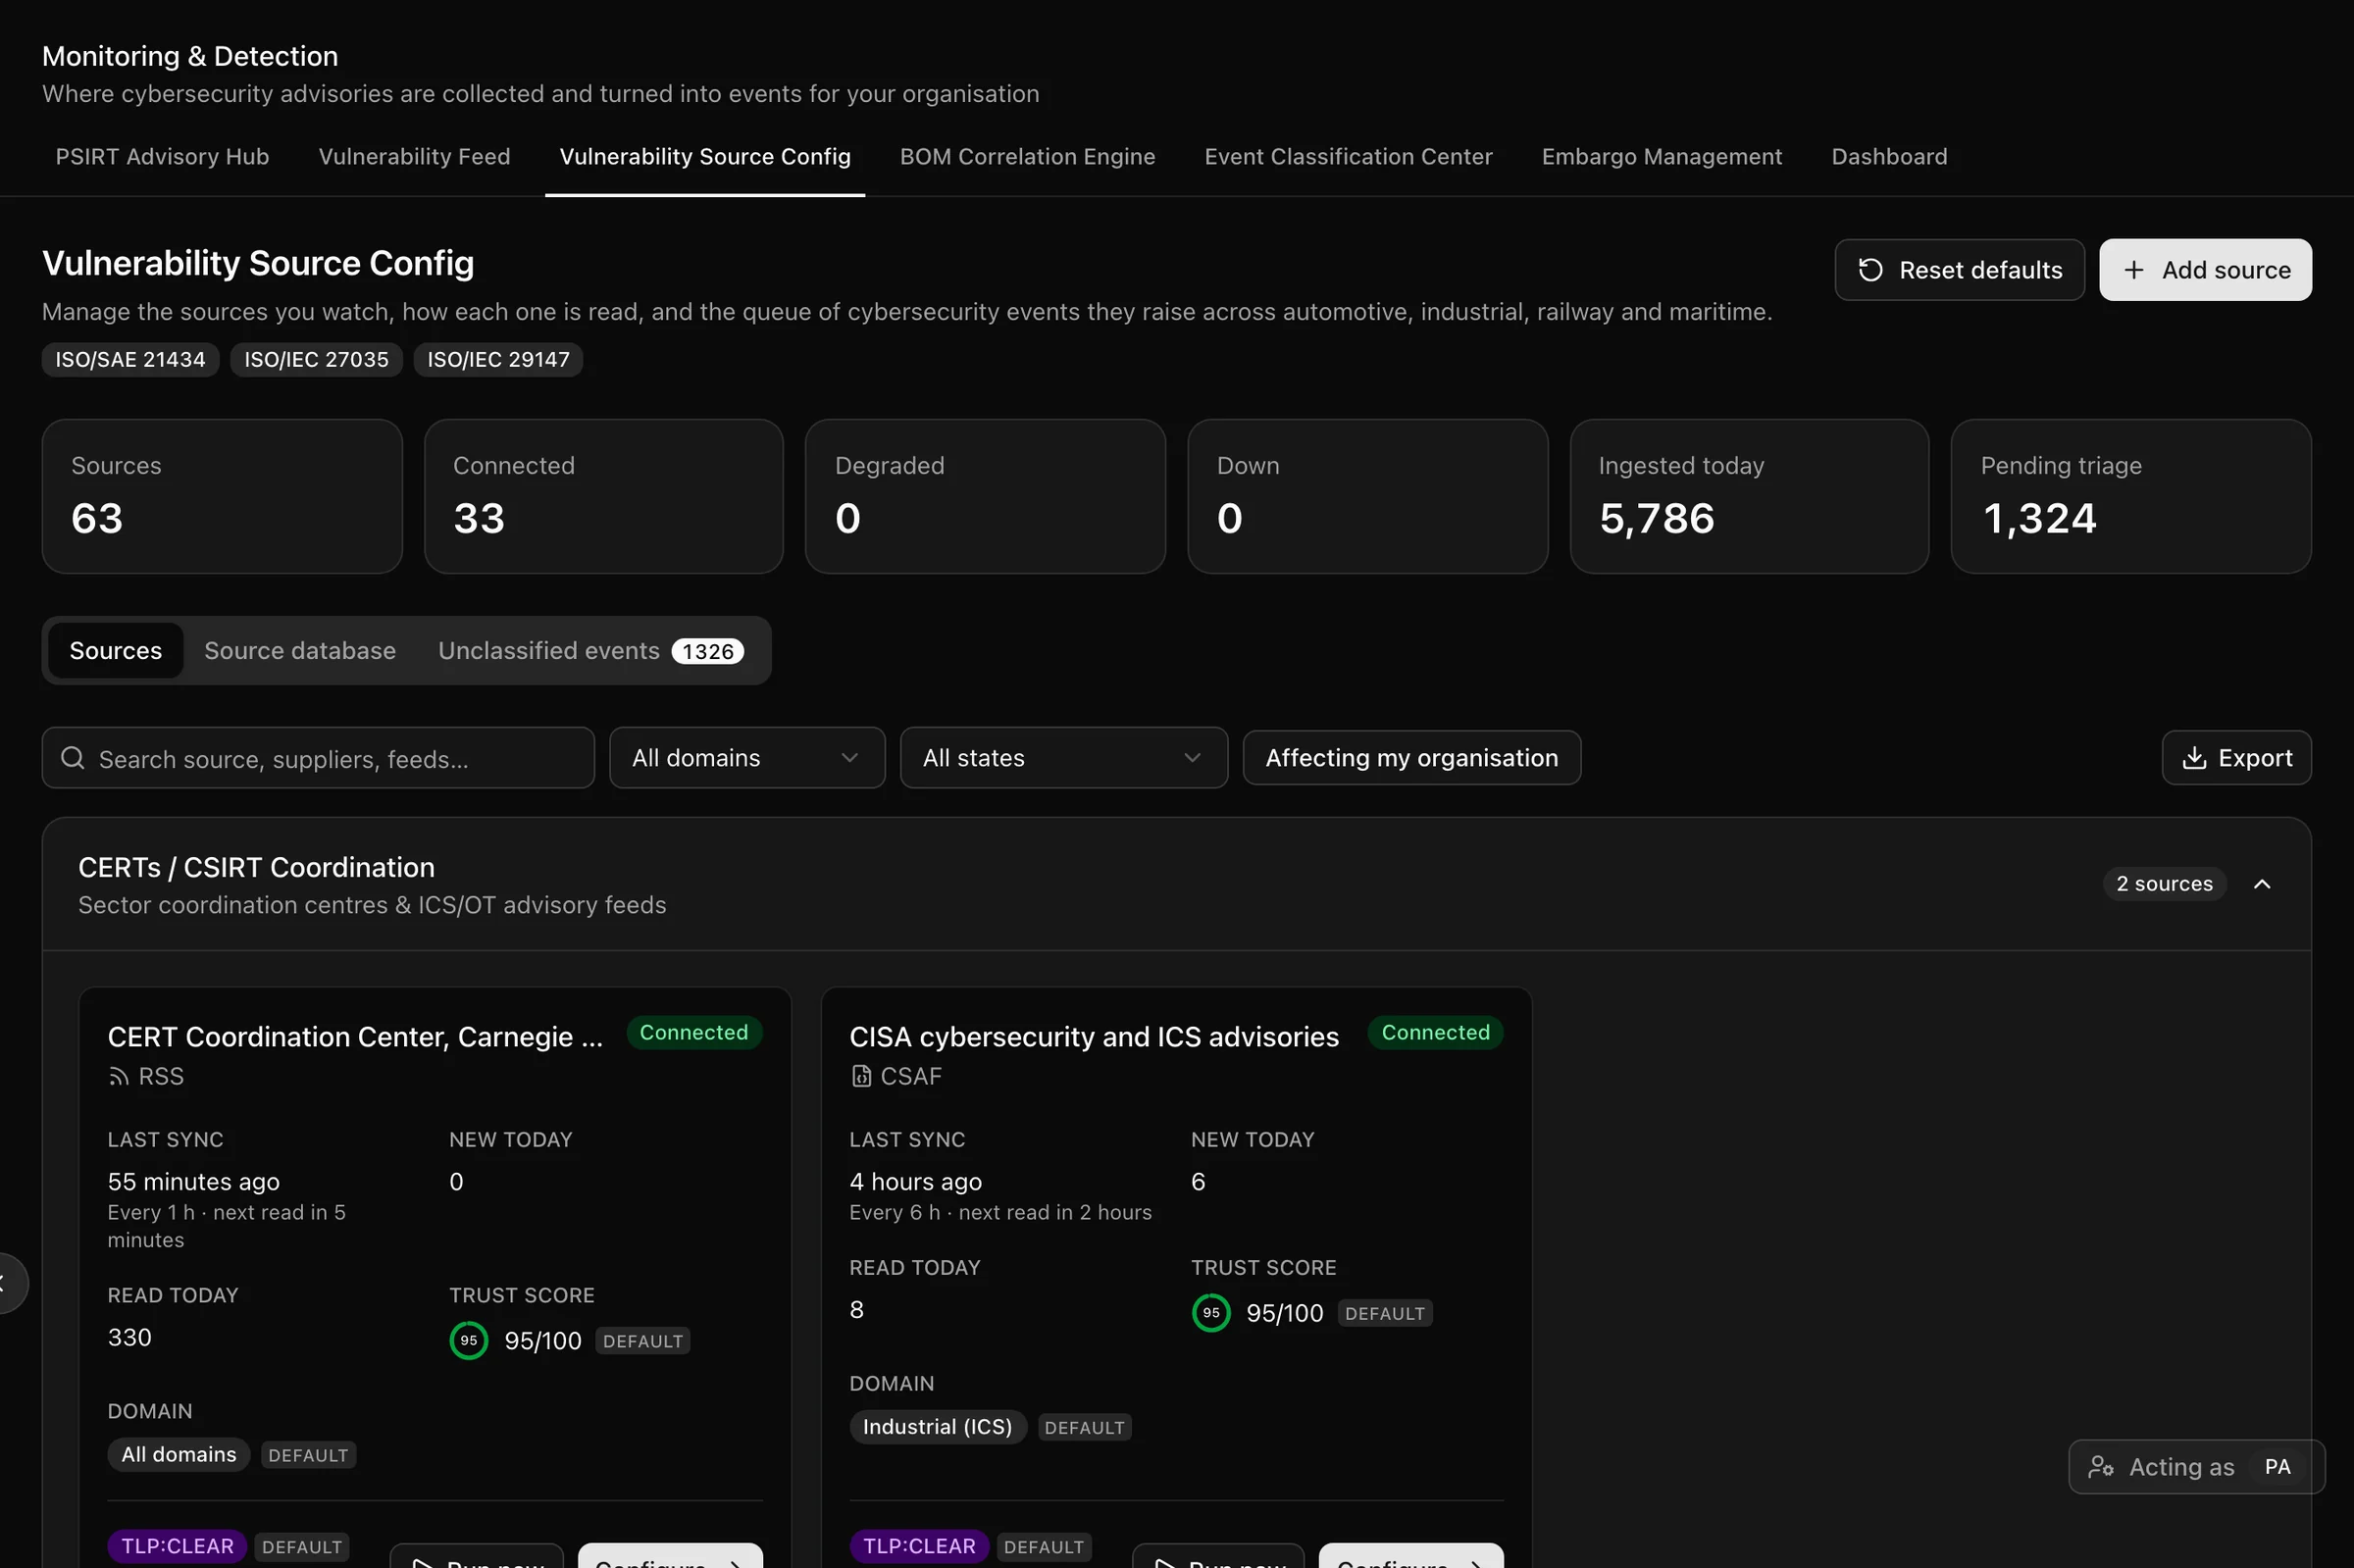
Reading a chip vendor PSIRT advisory
Affected parts, fixed versions and VEX statements, and what to do when a part is not listed.
 Regulation
The Cyber Resilience Act for component makers
Reporting duties, support periods and the SBOM, explained for teams that ship hardware.
Product updatesVariants without copying the analysis
Keep one baseline and let each market variant carry only what differs, with its own released revision.
EngineeringZones and conduits on a ship’s bridge network
Applying IACS UR E26 and E27 to an integrated bridge, from the shore link to propulsion control.