
Built for regulated industries
SecBerg Core adapts to the process, standards and compliance requirements of your industry, without changing how your teams work.
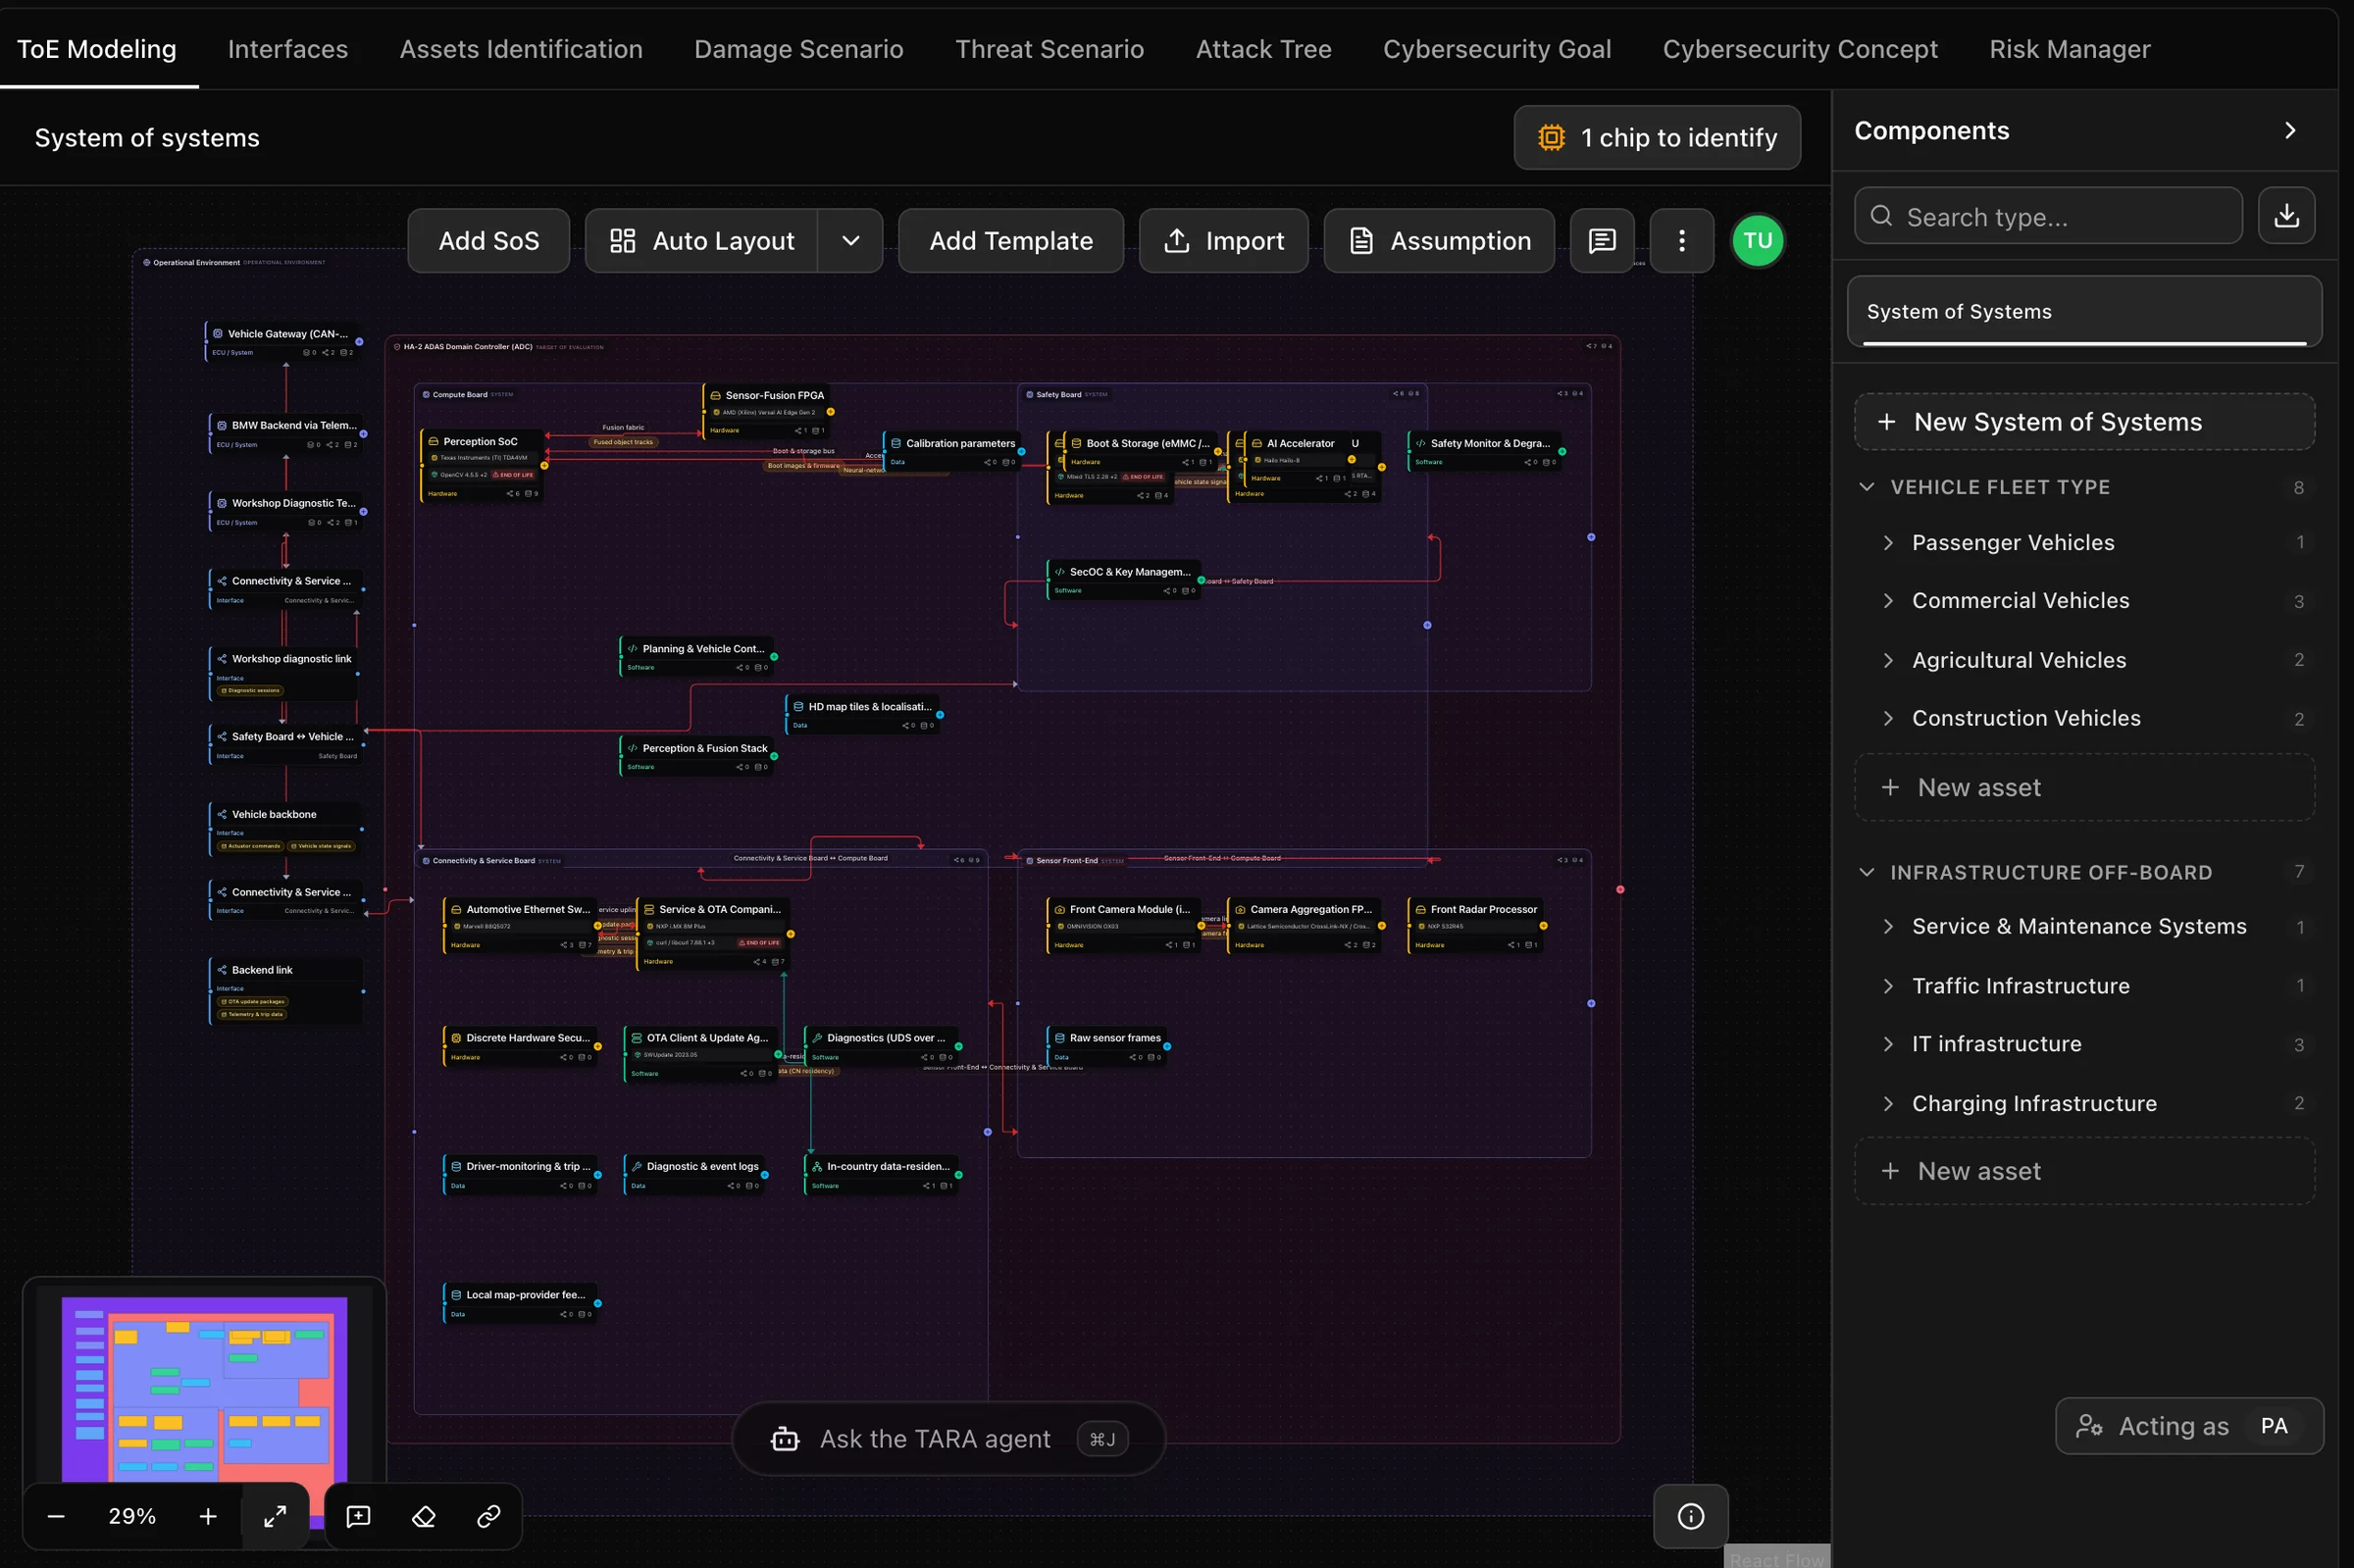
Automotive
For carmakers and their suppliers, from type approval to the last update in the field.
ISO/SAE 21434UNECE R155UNECE R156GB 44495AIS 189MLITASPICE for Cybersecurity
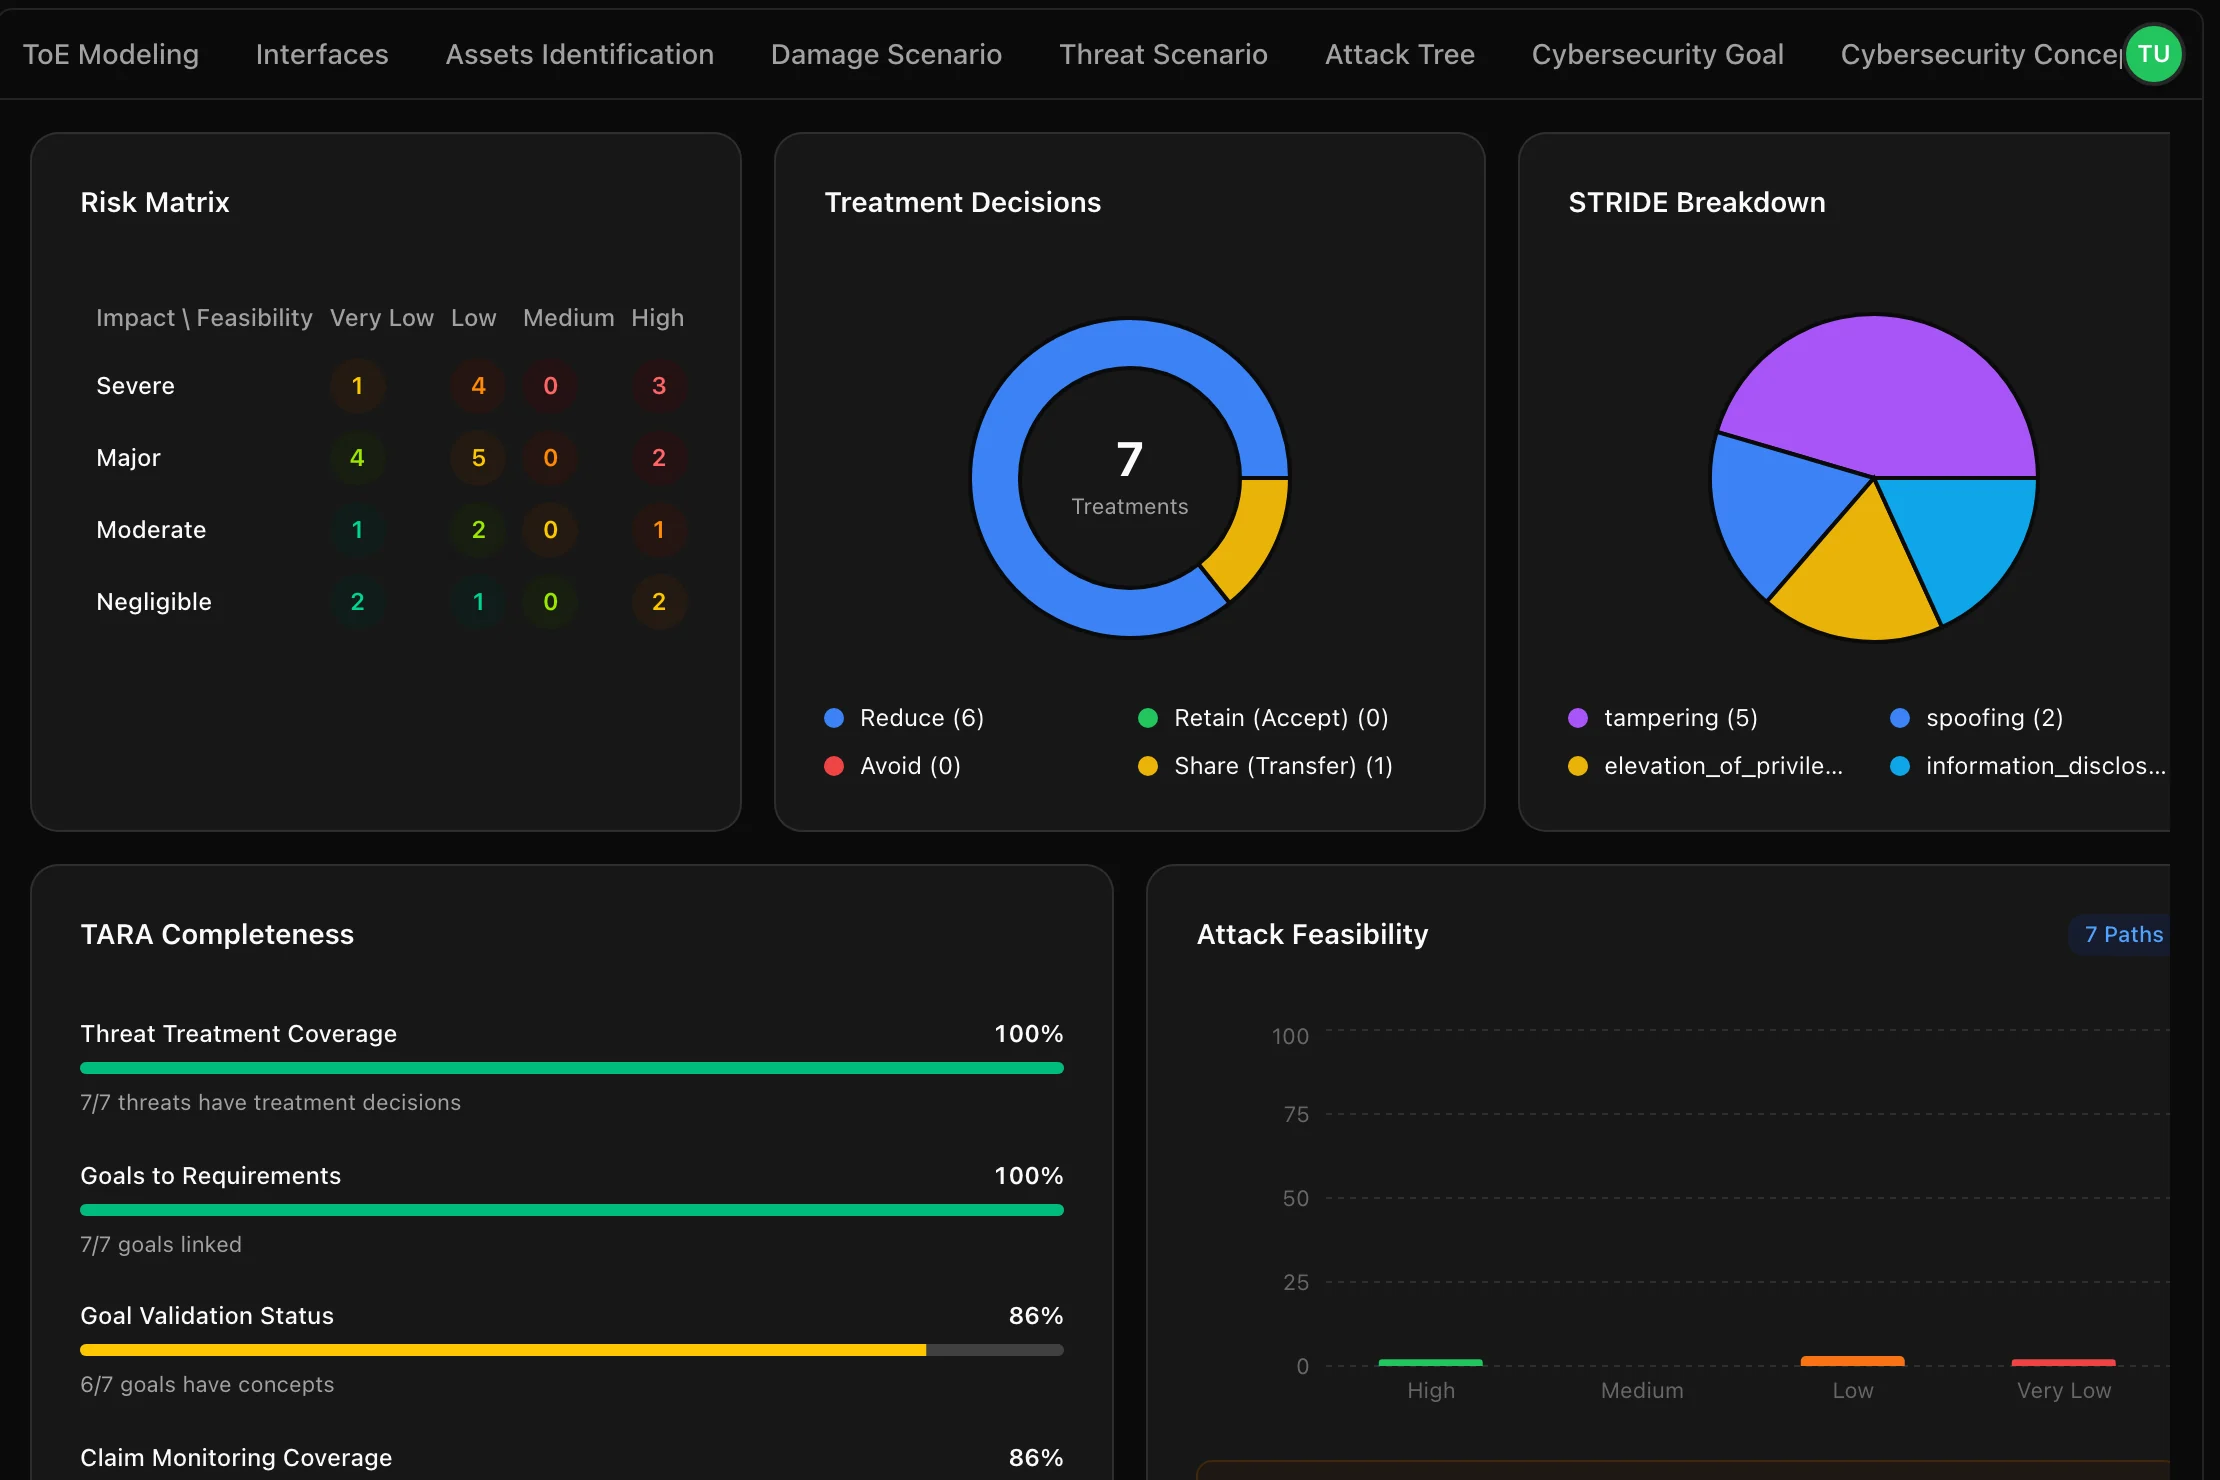
- TARA
- Cybersecurity architecture
- Requirements management
- Vehicle lifecycle security
Railway
For rolling-stock and signalling suppliers working to the rail cybersecurity standards.
CLC/TS 50701IEC 63452IEC 62443Cyber Resilience Act
- A framework for the full lifecycle
- Risk assessment
- Supplier management
- Train lifecycle security
- Cybersecurity maintenance
Maritime
For shipbuilders, ports and equipment makers meeting the IACS unified requirements.
IACS UR E26IACS UR E27IEC 62443-3-2
- Shipbuilders and ports
- Fleet lifecycle security
- Digital ship engineering
Robotics and manufacturing
For makers of industrial robots, autonomous systems and factory automation.
IEC 62443-3-2Cyber Resilience Act
- Industrial robots
- Autonomous systems
- Factory automation
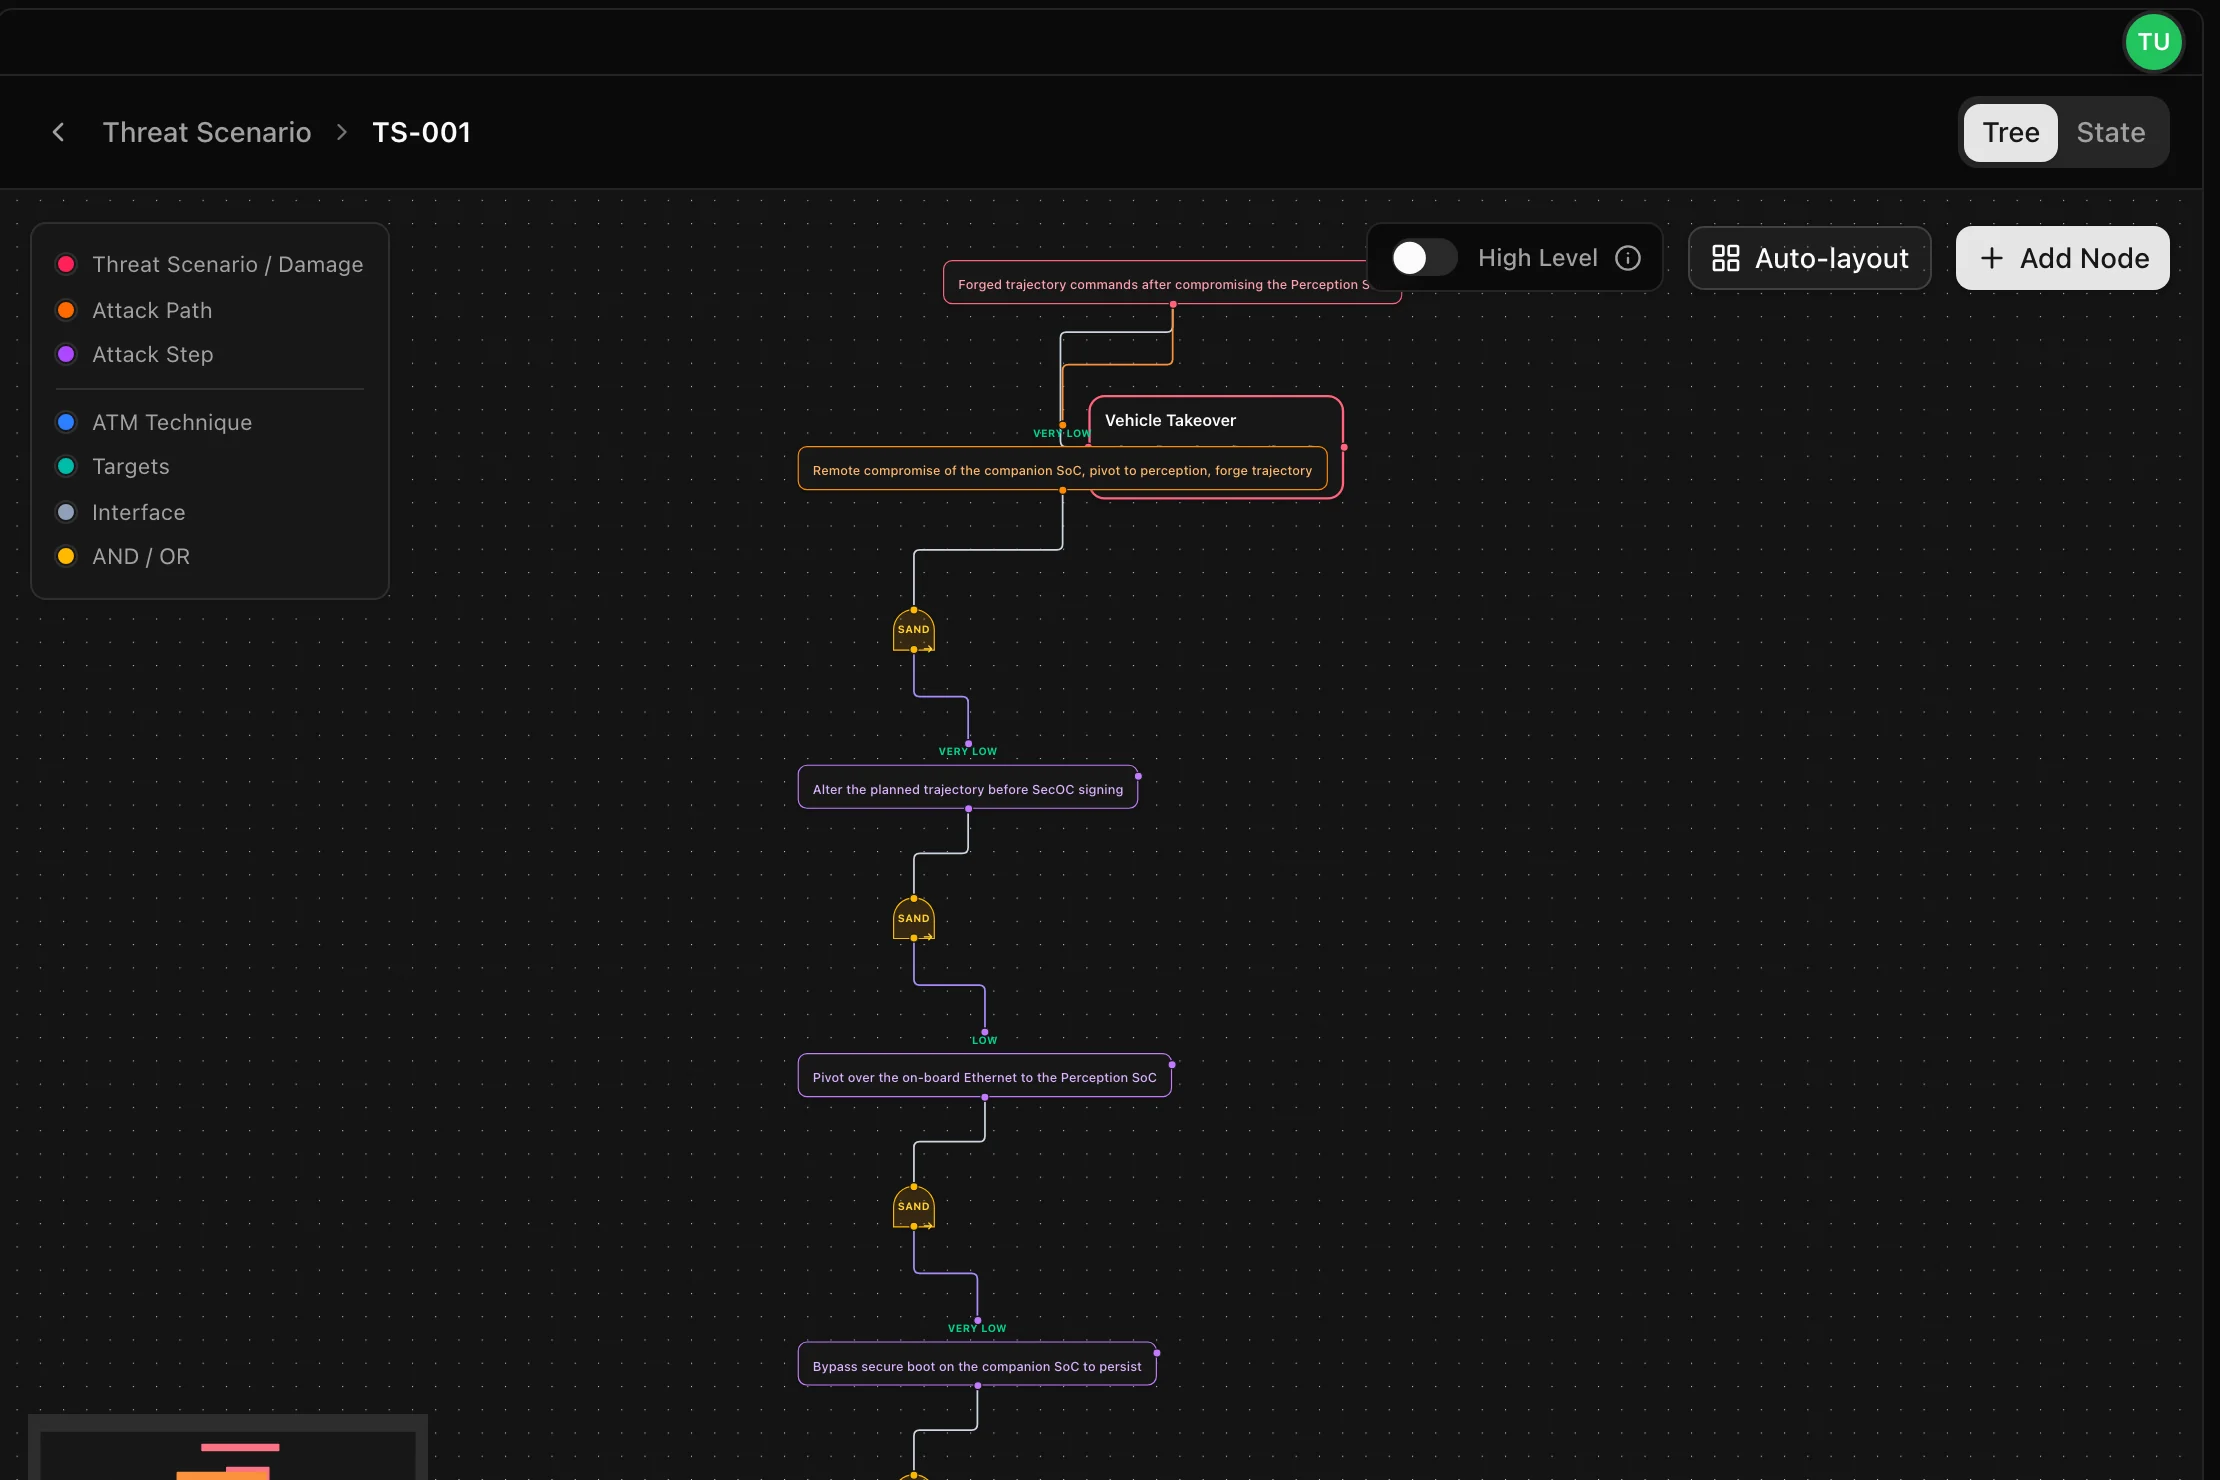
One platform, set to your standard
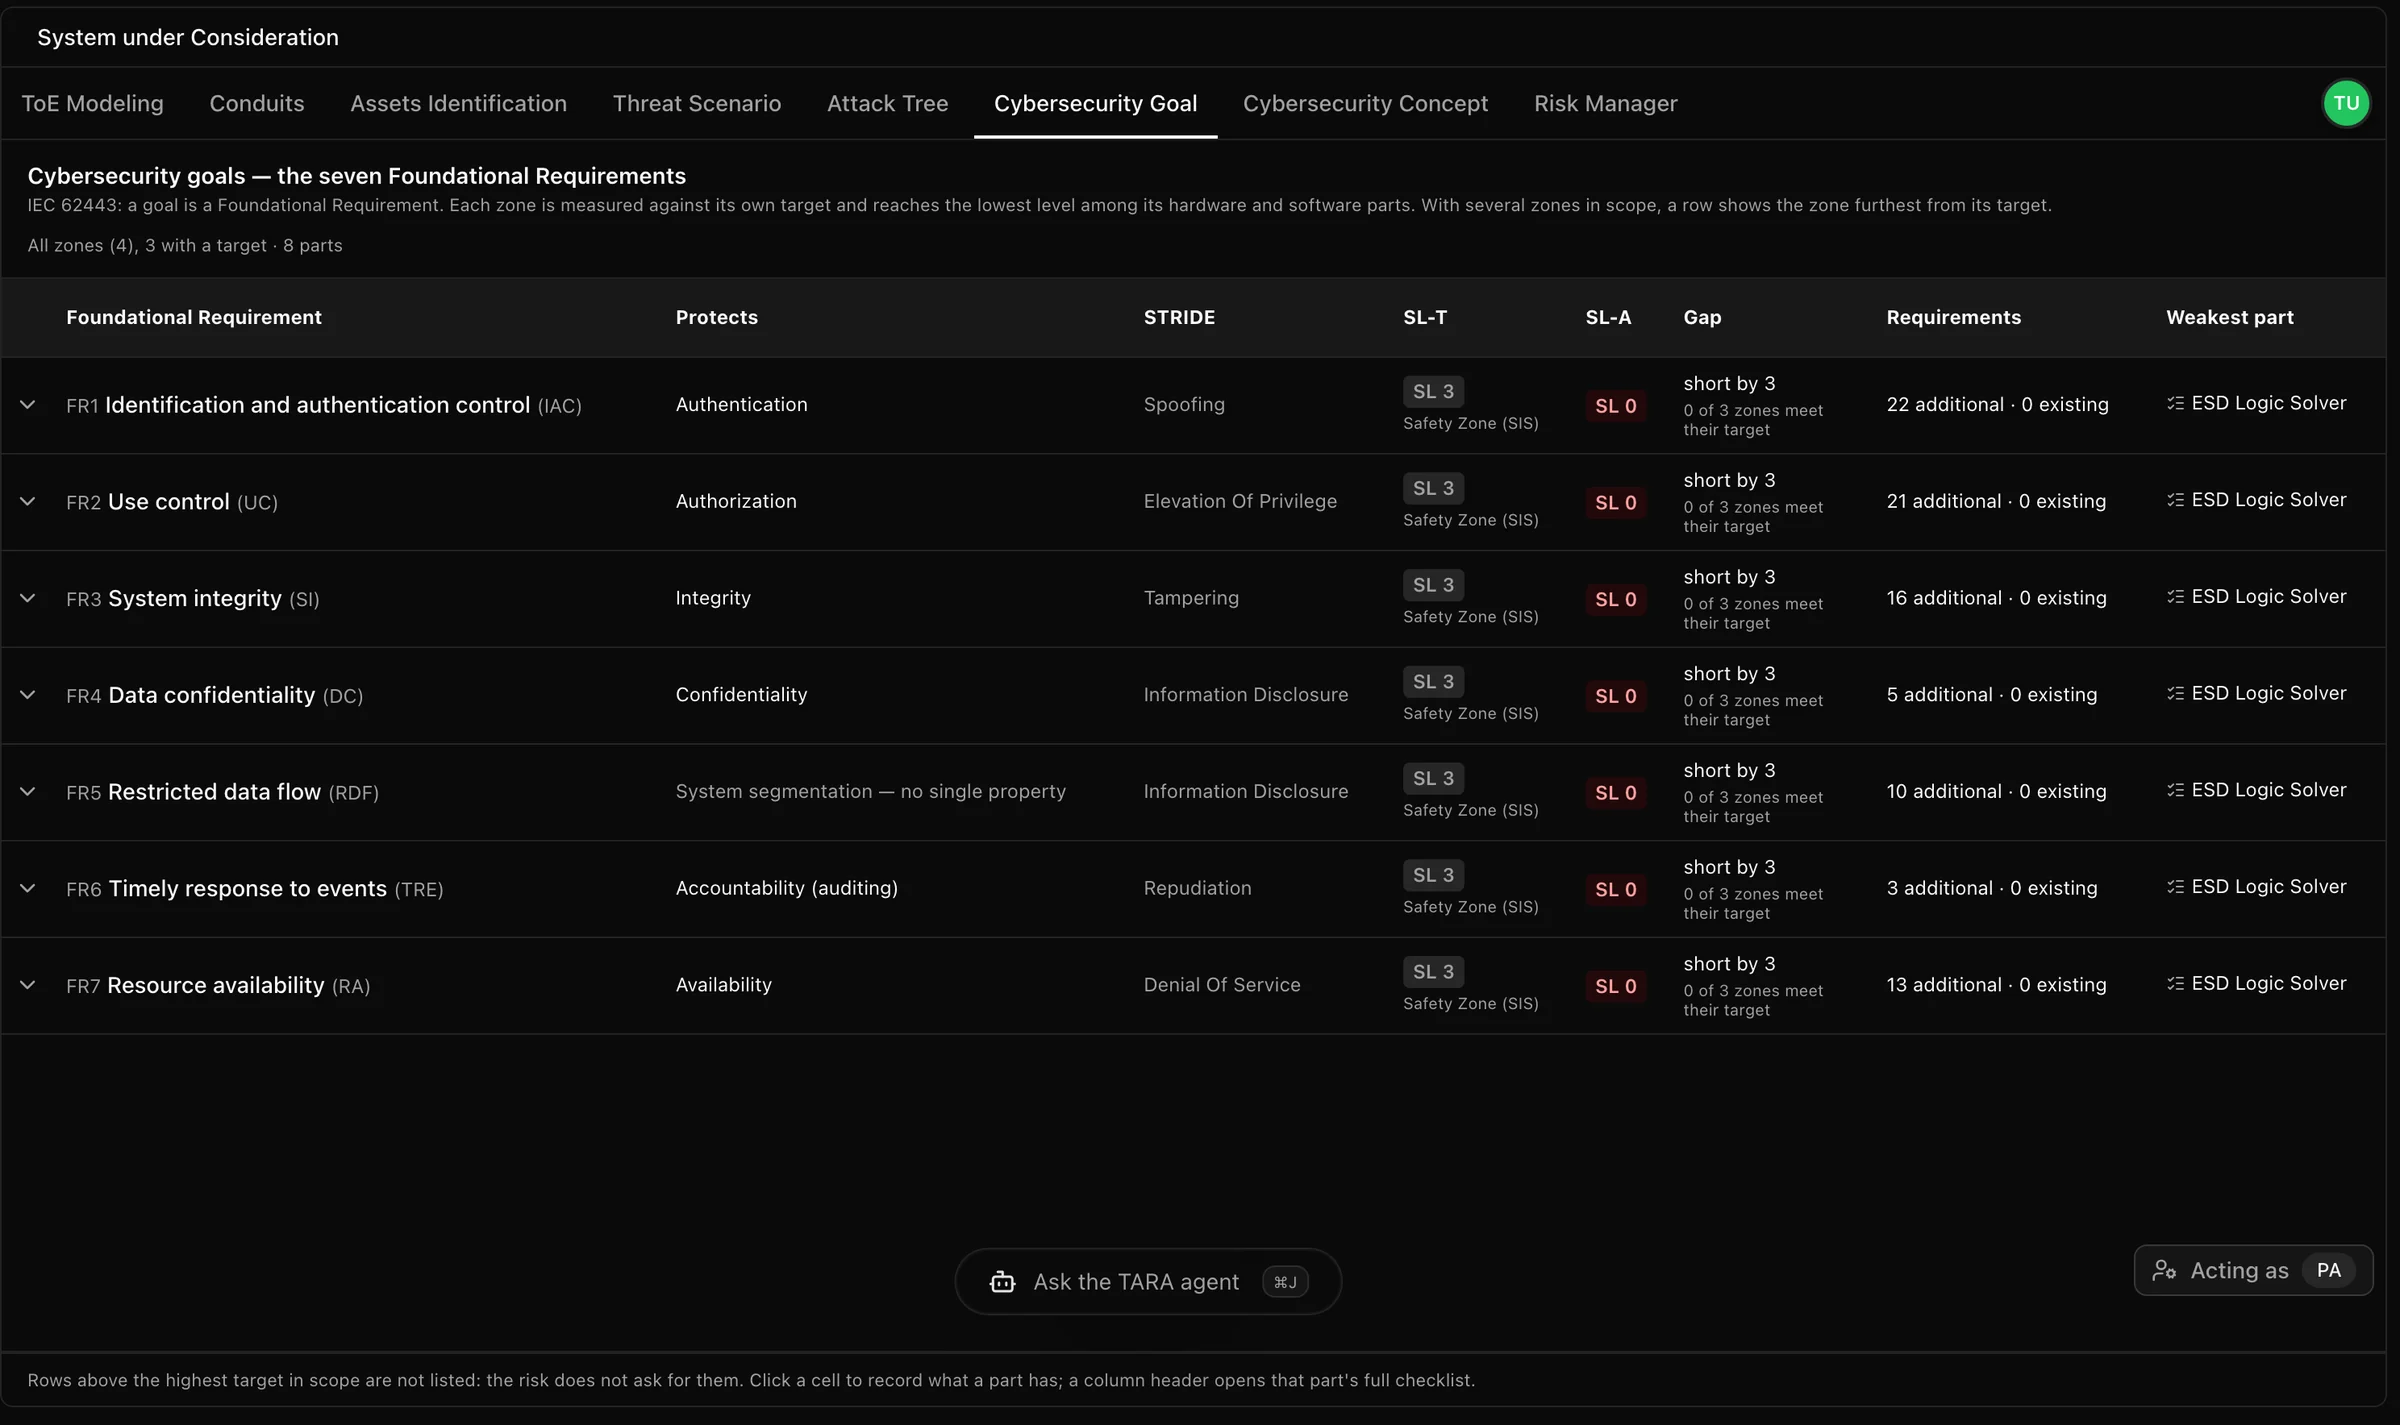
Switch the project from ISO/SAE 21434 to IEC 62443 and the same model is assessed the way your standard asks, with its own goals, levels and evidence.
Start with
one programme
Live within a month. Proven on real work within three.
- 01Book a workshopBring one programme and the standards it answers to.
- 02Model it togetherOur engineers build it with yours, live in the platform.
- 03Run the pilotReal work, real evidence, signed off in three months.